Review dangling DNS records by preserving the DNS response, tracing the target, and asking the service owner to confirm whether the dependency is still intended. A failed lookup or missing service is evidence for investigation, not proof that another party can claim the resource. This 2026 guide separates what you observed, what remains unknown, and what you can safely recommend to an MSP prospect.
- Dangling DNS records require ownership review; a failed lookup does not prove takeover eligibility.
- SCOUTz supports MSP prospect intelligence; public-domain evidence must stay separate from consented internal evidence.
- Keep DNS responses, collection dates, affected hostnames, and investigation limits attached to every finding.
- Verify remediation against a pinned baseline; unknown ownership remains unknown until the responsible owner confirms it.
How to review dangling DNS records without claiming a takeover
Treat the record as a dependency to verify, not an exploit to announce. Your evidence packet should let another practitioner reproduce the observation and understand its limits. The domain scan to first-call evidence packet workflow provides a related structure for carrying findings into discovery.
Preserve the published record
Record the hostname, record type, returned value, resolver or authoritative server queried, response status, and collection timestamp with its time zone. Preserve the raw response as well as your summary. DNS lookup behavior and response fields are defined in the DNS standards, including RFC 1034 and RFC 1035.
For a CNAME, capture the alias and its target. Follow the chain rather than stopping at the first answer. A hostname can resolve through several dependencies before reaching an address or a failure.
Include the TTL returned with each relevant response, expressed in seconds. That value helps explain caching; it does not establish how long the record has existed or when a provider resource was deleted.
Classify the response accurately
A negative answer, a lookup failure, and an application error describe different conditions. Keep them separate in the report.
| Observation | What it supports | What it does not establish | Best for |
|---|---|---|---|
| Target returns NXDOMAIN | The queried name did not exist in that DNS response | Provider resource claimability or attacker control | Investigating a potentially stale dependency |
| NOERROR with no requested record in the answer | The lookup returned no record of the requested type | That the name itself is absent | Checking record-type assumptions |
| SERVFAIL or timeout | The lookup failed or did not complete | That a service was deleted | Investigating resolution or collection problems |
| Provider-branded error page | The service returned that response at collection time | That another account can register the resource | Requesting provider-side ownership verification |
| Owner confirms retirement | The dependency is no longer intended | That removing it has already resolved every dependency | Planning authorized cleanup |
Each observation has a use and a limit. None of these observations alone confirms a takeover.
Trace the dependency without claiming it
Identify the apparent service provider and the target naming pattern. Separate an inference based on a hostname from provider documentation or evidence supplied by the owner.
Provider-specific resource binding determines whether an abandoned reference creates a takeover opportunity. A resource name that appears unused can still require domain verification, remain reserved, or be unavailable for reassignment. An error-page signature does not answer those questions.
Do not register a resource, attach the prospect's hostname to your account, publish content, or request a certificate as part of routine sales preparation. Those actions change the activity from observation to an attempted exercise of control. Any authorized validation needs explicit scope and a separate decision.
Confirm intent with the responsible owner
Ask who controls the DNS zone and who owns the referenced service. Those responsibilities can sit with different teams, an agency, a former supplier, or a customer administrator.
Request confirmation of the intended use and current resource binding. A provider-console record, an approved change record, or an owner-confirmed retirement decision supplies context that public DNS cannot provide.
Keep your question narrow: whether the specific hostname should still point to the recorded target. Avoid treating uncertainty as evidence of neglect or an unresolved security problem.
Record the boundary and next choice
Separate the condition, affected object, unknowns, and recommended outcome. Let the MSP choose the service, process, project, or decision to take no action.
A defensible finding contains:
- Condition: the published record and the response observed during the review.
- Evidence: the source, collection date, raw response, and relevant target chain.
- Boundary: ownership, claimability, and exploitation status that remain unverified.
- Owner: the person or team responsible for deciding the hostname's intended use.
- Next choice: verify the binding, investigate a lookup failure, or approve retirement.
For your 2026 review template, make the collection timestamp mandatory. A finding without its run date loses the context needed to assess freshness.
Verify the approved outcome
Pin the original evidence before any change. After the owner approves remediation, repeat the relevant checks and compare the result with that baseline.
Check the intended service outcome as well as the DNS change. Removing an alias is not a successful outcome if an active customer portal still depends on it.
Record what changed, who approved it, when you checked again, and which dependencies remain outside the review. Proof is the comparison against the baseline, not a closed ticket alone.
Why this matters
An MSP sales conversation needs a condition the prospect can verify and a next choice the prospect can own. Calling an ambiguous DNS response a takeover damages that conversation before discovery begins.
Public DNS provides external observations. It does not establish account ownership, internal application dependencies, or the prospect's willingness to buy a service. Your useful output is a dated question supported by evidence.
The same boundary applies when discussing Microsoft 365. Public-domain evidence cannot establish Conditional Access coverage, application permissions, license assignments, device state, or tenant sharing configuration. Those require appropriate customer-authorized evidence.
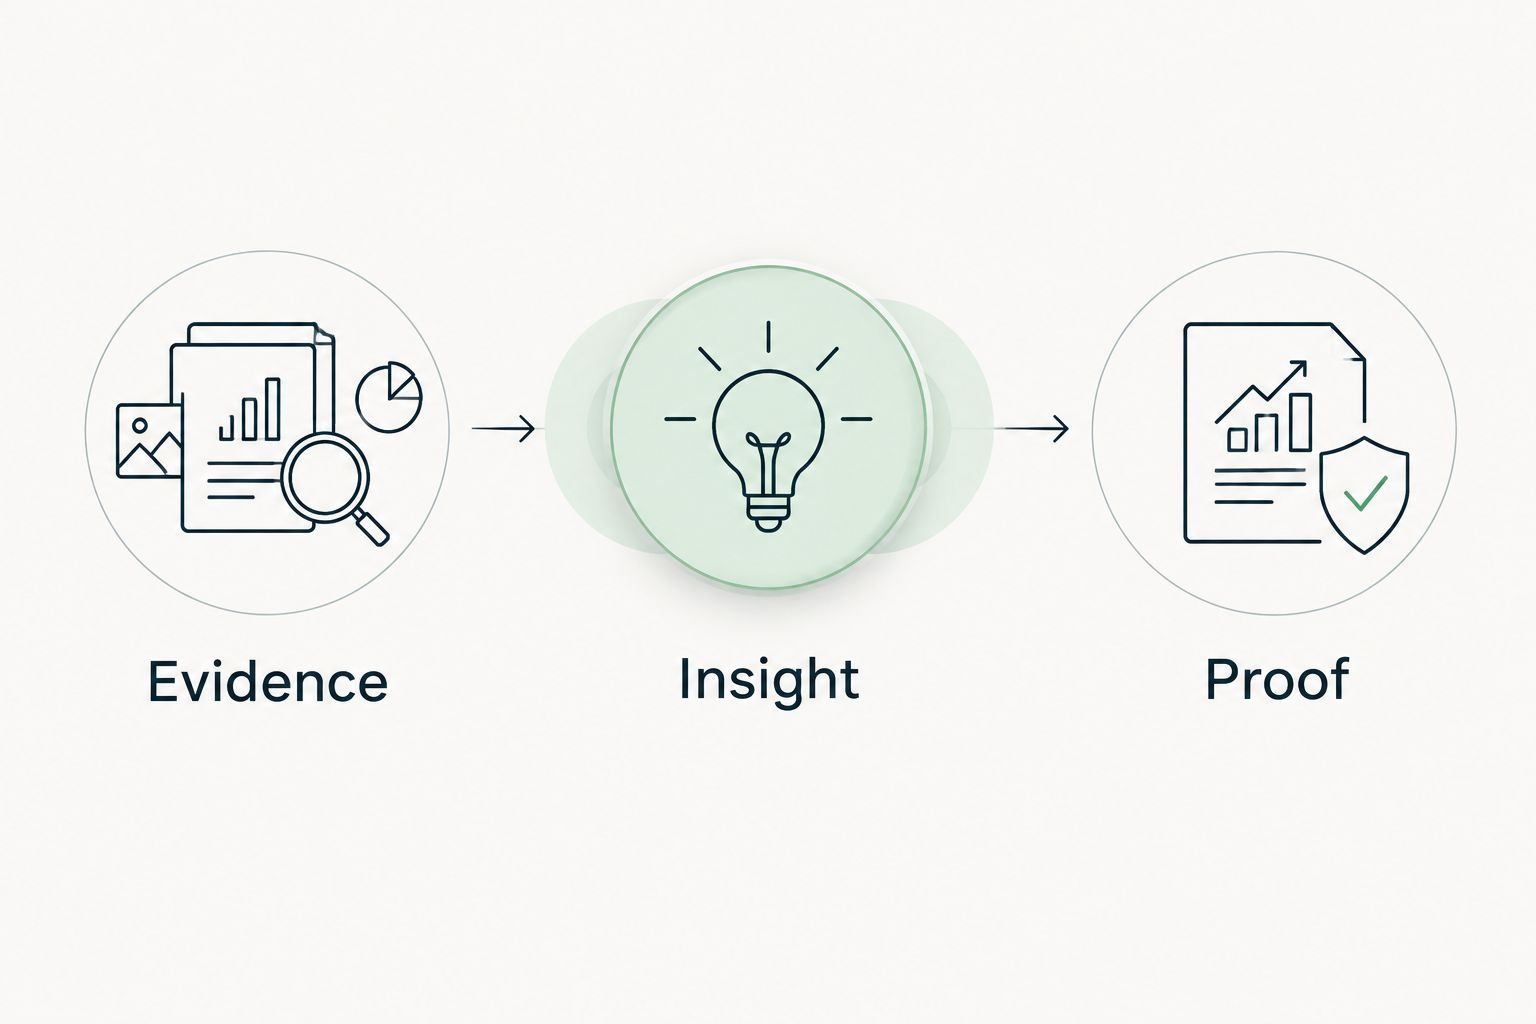
Evidence, insight, and proof belong in separate fields
Use a report structure that preserves the distinction between collection, interpretation, and verification. The following is an illustrative workflow, not a customer finding.
- Evidence: preserve the published alias, target response, source, and run date.
- Insight: explain the possible consequence and ask whether the dependency remains intended.
- Proof: compare an authorized rescan with the pinned baseline after an approved change.
The possible consequence must remain conditional on the missing facts. If an external provider permits another account to bind the abandoned resource, the hostname can create a takeover risk. Public DNS alone does not establish that permission.
Keep the evidence state distinct from coverage. Observed describes a collected condition; Inferred describes an interpretation; Unknown describes an unanswered question. These labels are not a progression toward a confirmed incident.
Coverage answers a different question: what the review actually assessed. A public DNS review can be Assessed while provider-side ownership remains Not assessed. A collection failure belongs in the limitations, not in a clean result.
In a 2026 client-safe report, put the limitation beside the finding. A separate disclaimer at the end is too easy to detach when someone forwards a slide or copies a paragraph.
Why dangling DNS findings vary
The same visible symptom can require different follow-up. These factors explain why a generic scanner label is insufficient:
- Record type: an alias, address record, or name-server delegation creates a different dependency and needs its own investigation path.
- Provider binding: the provider's ownership-verification and resource-reassignment rules determine what an external party can actually do.
- Lookup vantage: resolver caches and authoritative answers can differ during changes or failures; preserve where each answer came from.
- Service intent: a deliberately retired hostname needs a different decision from an active hostname with a resolution fault.
- Ownership evidence: public records rarely answer who controls the referenced provider account or whether a resource remains reserved.
- Authorization scope: passive observation, application requests, and attempted resource registration are different activities with different boundaries.
Match the recommendation to the evidence you have. When ownership is unknown, request ownership verification. When a service is confirmed retired, request an approved cleanup decision.
Keep public observation separate from authorized validation
For prospect research in 2026, define the permitted activity before collection. Public visibility does not establish blanket permission for active probing, and this workflow is not legal advice.
A routine public-domain review should stop short of resource registration or control demonstrations. Offer any additional validation as an opt-in activity with the owner, scope, method, and stop conditions agreed in advance.
Customer authorization also has limits. Permission to review one hostname does not automatically extend to related domains, provider accounts, or application content. Record the boundary with the finding so a later technician does not expand the test based on a sales note.
If an unexpected response exposes information, avoid collecting unrelated material. Preserve only the evidence needed to describe the condition and follow the agreed reporting process.
Turn the finding into a discovery question
The useful sales question concerns ownership and intended use. Ask who maintains the hostname, whether the referenced service remains required, and what evidence would settle the decision.
Do not convert a technical observation into buying intent. A prospect can acknowledge a stale record and still decide to resolve it internally, defer it, or investigate further.
SCOUTz is best for MSPs preparing prospect conversations with dated cybersecurity evidence. SCOUTz prospect intelligence supports that preparation; the relationship and sale stay with the MSP. Public-domain observations remain separate from customer-authorized, read-only Microsoft 365 configuration and metadata evidence.
Next step: Join Open Beta for evidence-led MSP sales preparation. The product's role is to prepare the conversation, with the MSP responsible for the interpretation and next choice.
Does a dangling CNAME prove a subdomain takeover?
A dangling CNAME does not prove a subdomain takeover. It establishes a reference that needs investigation when its target appears absent or disconnected.
A takeover claim needs evidence about the provider's binding rules and actual control. Keep that distinction explicit even when a scanner assigns a severe label.
Should you delete a dangling DNS record immediately?
Delete a dangling DNS record only after the responsible owner approves the intended outcome. Verify that an active service or recovery process does not still depend on the hostname.
Preserve the baseline first. Then confirm both the published DNS result and the intended service behavior after the change.
Can a public DNS review prove that a tenant is secure?
A public DNS review cannot prove that a tenant is secure. It provides evidence about the public records and endpoints actually assessed.
Internal configuration and metadata require appropriate authorization and access. Keep unread sources explicitly unknown, including in an otherwise reassuring report.
FAQ
What are dangling DNS records?
Dangling DNS records are references to resources that no longer exist or are no longer correctly bound to the intended service. A failed lookup is a reason to investigate that condition, not automatic proof that the reference is exploitable.
Does NXDOMAIN mean someone can take over my subdomain?
NXDOMAIN does not establish takeover eligibility. It reports that the queried name did not exist in that DNS response; provider resource ownership and reassignment rules require separate evidence.
Can I confirm a takeover from an error page?
An error page alone cannot confirm a takeover. Preserve the response and collection date, then request authorized verification of the resource binding and provider requirements.
What should an MSP put in a dangling DNS finding?
An MSP should include the affected hostname, record type, target, raw response, collection timestamp, source, and investigation limits. Keep the possible consequence separate from the observed condition and identify the owner of the next decision.
Should I claim an abandoned resource to prove the problem?
Do not claim an abandoned resource during routine prospect research. Any control validation needs explicit authorization, a defined scope, and agreed stop conditions.
How do I verify a dangling DNS fix?
Verify a dangling DNS fix by repeating the relevant checks against a pinned baseline and confirming the intended service outcome. Record the approval, changed evidence, rescan date, and remaining unknowns.
Can public DNS evidence replace a Microsoft 365 review?
Public DNS evidence cannot replace a customer-authorized Microsoft 365 review. It does not establish internal controls such as Conditional Access coverage, application permissions, or tenant sharing configuration.
One last thing
A green result can be as misleading as an alarming one. If the collector could not read a source, the result is unreadable, not evidence that the control is present or the risk is absent.
For your next 2026 report, make that distinction visible beside every affected finding. SCOUTz's evidence-led approach keeps what ran, what remains unknown, and what changed attached to the conversation.