All articles
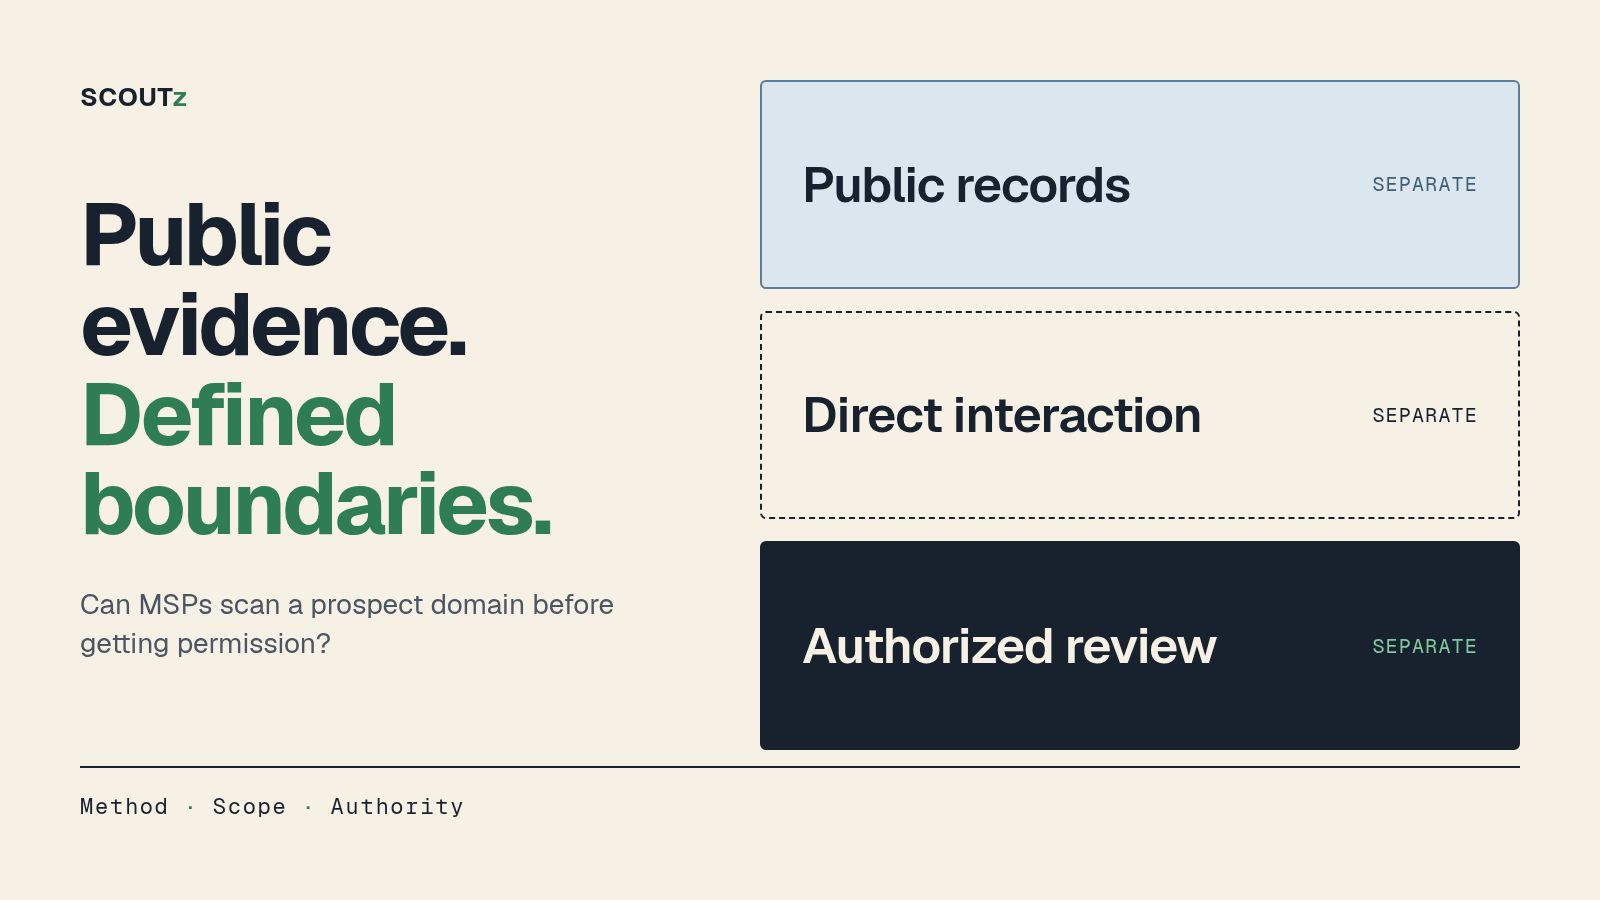
Can MSPs scan a prospect's domain before getting permission?
Public records and direct security tests are different activities. Review authorization, federal and state law, evidence limits and MSP outreach requirements.
BLEditorial TeamOct 27, 2026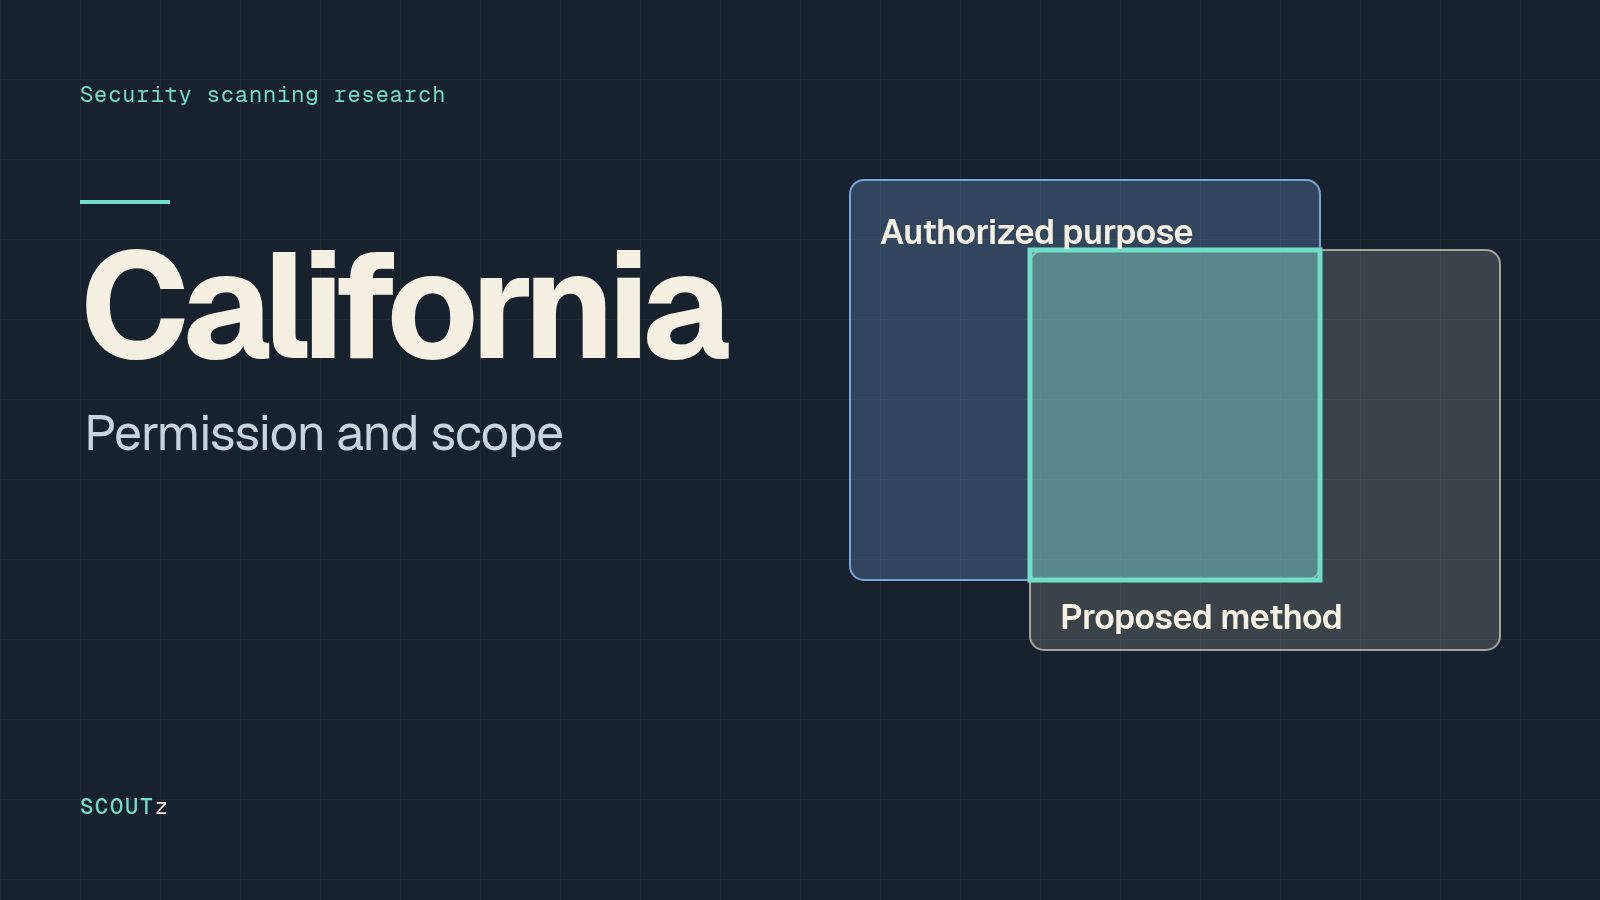
California security scanning laws: permission, service use and loss
Review California Penal Code 502 on access, computer services and civil loss. Read-only operations do not by themselves establish permission.
BLEditorial TeamOct 27, 2026
MSP sales training: coach evidence-led conversations with SCOUTz
Use SCOUTz reports, findings and work context to train MSP sales teams on evidence-led discovery, consent, scope and technical handoffs.
BLEditorial TeamOct 27, 2026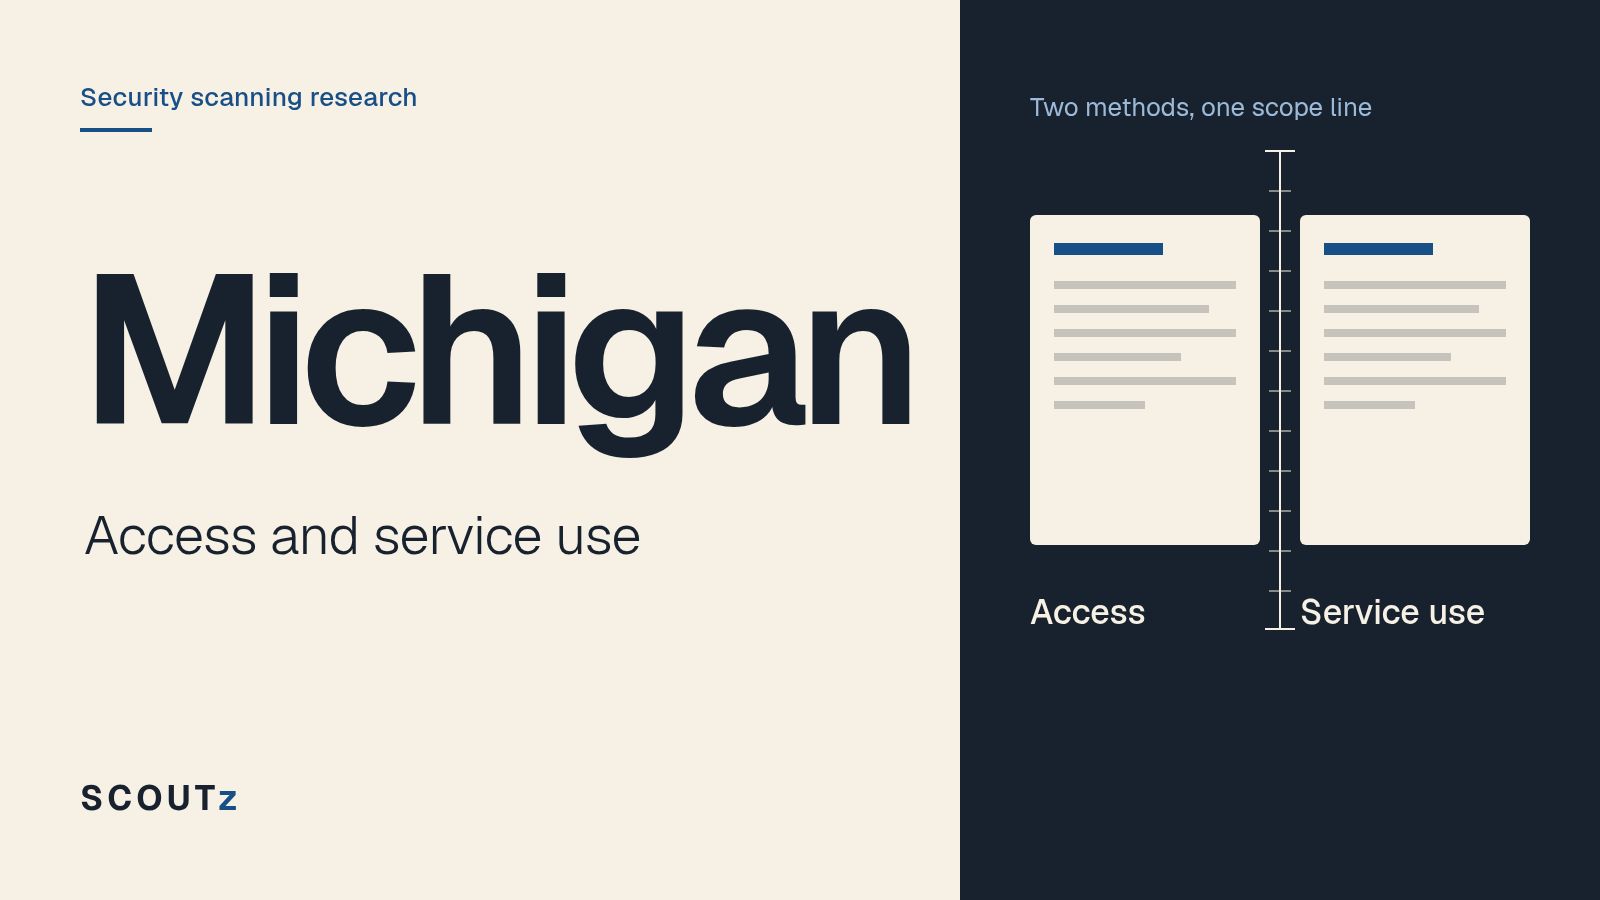
Michigan security scanning laws: access and computer-service use
Review Michigan security scanning laws, computer-service use and aggregate loss. Keep public-source evidence, permission and civil claims distinct.
BLEditorial TeamOct 27, 2026
How should MSPs compare monthly Microsoft 365 assessment quotes?
Compare monthly Microsoft 365 assessment quotes by collection, interpretation, reporting and remediation. Match the scope before comparing provider fees.
BLEditorial TeamOct 27, 2026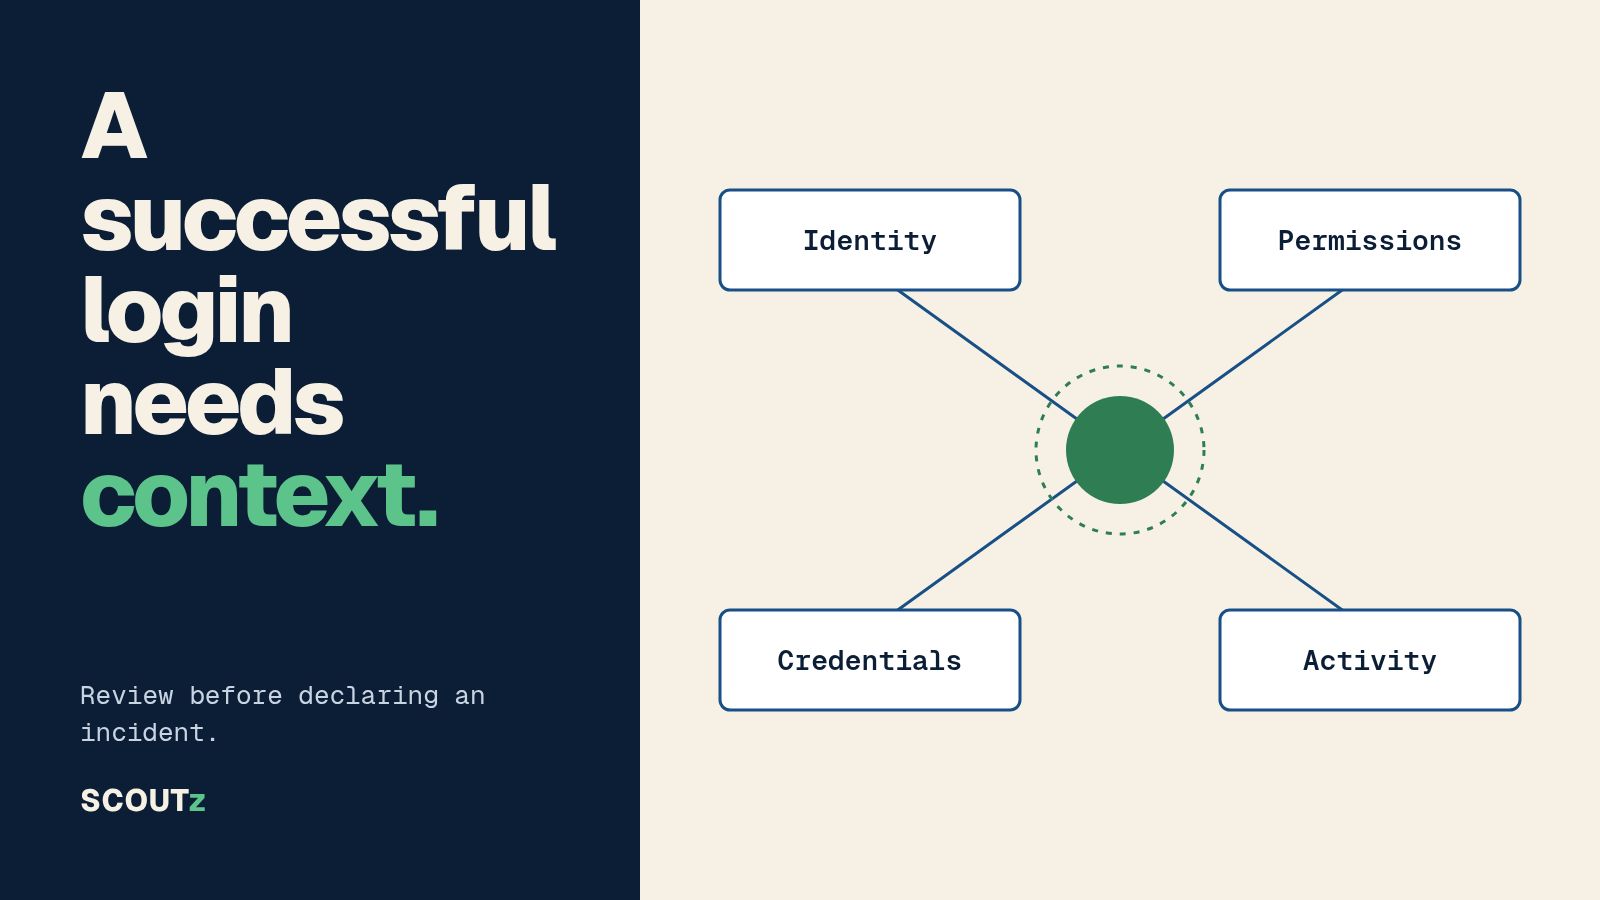
Does a service-principal login success alert mean an attack?
A service-principal login success alert can be routine or hostile. Here is the identity, permission and activity evidence that tells them apart.
BLEditorial TeamOct 27, 2026
Why MSP prospects go quiet after the first meeting
A useful MSP follow-up gives the buyer a decision, not another pitch. Send dated evidence, record what remains unknown, and agree on an owner for the next step.
BLEditorial TeamOct 27, 2026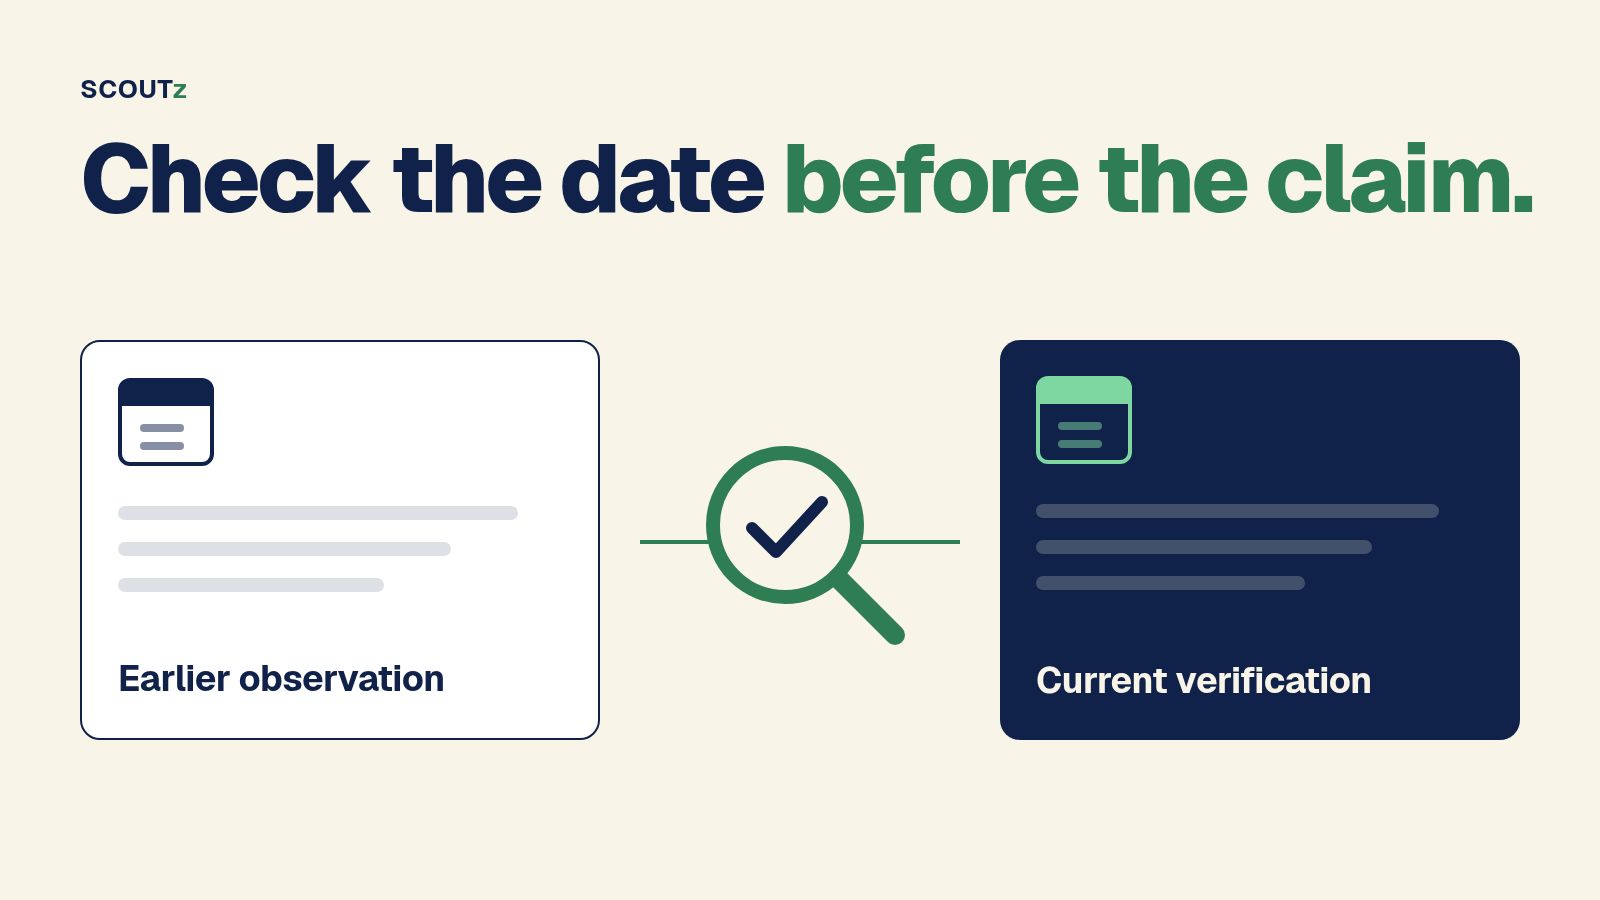
How to spot outdated findings in a security sales deck
Spot outdated findings in a security sales deck by checking dates, sources and coverage. Refresh the evidence before turning an old observation into a claim.
BLEditorial TeamOct 27, 2026
MSP enterprise sales: build an evidence packet buyers can review
Prepare MSP enterprise sales evidence with dated observations, clear limits and delivery ownership. Build a proof packet buyers and procurement can inspect.
BLEditorial TeamOct 27, 2026
MSP application reviews: connect permissions, ownership and purpose
An Applications Center for MSPs should connect permissions, licenses, AI features, history and trust. Review each client app without treating unknowns as clean.
BLEditorial TeamOct 27, 2026
Is a cybersecurity risk assessment tool worth it for a solo MSP?
Is a cybersecurity risk assessment tool worth it for a solo MSP? Use dated evidence, clear scope, and practical follow-up to decide without breach-cost claims.
BLEditorial TeamOct 27, 2026
How to interpret Microsoft 365 guest access findings for clients
Learn how to interpret Microsoft 365 guest access findings for clients: separate identity from access, explain evidence limits, and agree on verified actions.
BLEditorial TeamOct 27, 2026