Dark web monitoring cost per client depends on the supplier's billing unit, your contract commitments, and the work your MSP includes after an alert. Calculate the monitoring subscription allocation plus client-specific review, communication, and response work; a subscription-only comparison leaves those service costs outside the decision.
- For how much does dark web monitoring cost per client, compare supplier scope and MSP service work together.
- SCOUTz supports MSP prospect preparation; evaluate ongoing dark web monitoring separately.
- A breach-data match is evidence to review, not confirmation that a user is compromised.
- Define alert ownership and response boundaries before agreeing to a recurring service.
Why this matters
Your client buys an agreed service. Your supplier bills against a contract. Those scopes need to match before you put a recurring line into a proposal.
For a 2026 purchasing decision, start with the dark web monitoring tools for MSPs comparison, then request written terms for your actual client portfolio. A feature list cannot establish who investigates a match, contacts an employee, or verifies that an agreed action happened.
The useful distinction is between finding information and taking responsibility for it. Monitoring creates an input to a service process. Your agreement defines the process and its owner.
How much does dark web monitoring cost per client?
Calculate per-client cost from the supplier commitment and the service you will deliver, rather than from an alert count. Use the same scope and billing period for every quote you compare.
A practical calculation is:
Per-client delivery cost = allocated supplier cost + client-specific monitoring charges + review labor + communication labor + agreed response labor.
Include shared administration in the allocation. Keep separately approved incident work outside the recurring calculation unless your agreement explicitly includes it.
| Cost component | What to establish | Boundary to record |
|---|---|---|
| Shared supplier commitment | Contract minimum, billing period, included coverage | Which clients carry the shared allocation |
| Client-specific coverage | The contracted unit and enrolled scope | Domains, identities, or other covered objects |
| Review work | Who validates relevance and records the evidence | What an alert can and cannot establish |
| Client communication | Who receives findings and approves action | Notification route and decision owner |
| Response work | Which actions the recurring service includes | Where separately authorized work begins |
| Reporting and verification | What gets reported and how completion is checked | Evidence retained and review date |
For an annual commitment, divide the annual obligation by 12 months before comparing it with monthly commitments. For labor, convert recorded minutes to hours using 60 minutes per hour, then apply your internal labor-cost method. These are calculation units, not estimates of how long an alert takes.
Keep the denominator explicit. A calculation for 1 client must include that client's allocated share of any supplier minimum, rather than assuming every contracted slot is already assigned.
Separate delivery cost from the client quote
Your delivery cost is the internal resource requirement. The client quote also reflects the scope you agree to take on and your commercial terms.
Do not call a supplier subscription your fully managed service cost. Equally, do not put every possible incident into a recurring monitoring promise. Define included work, exclusions, approval requirements, and escalation before presenting the agreement.
Revisit the calculation when coverage changes. Adding identities, domains, reporting requirements, or response obligations changes the service you must deliver even when the subscription arrangement stays the same.
Compare service scopes before comparing suppliers
A monitoring feed and a managed review service perform different jobs. Compare each option against what the buyer wants your MSP to own.
The following scopes are proposal choices, not claims about any supplier's package or availability.
| Proposed scope | Best for | What you agree to deliver | Limitation |
|---|---|---|---|
| Monitoring and notification | Clients with an internal investigation owner | Enrollment, alert routing, and agreed notifications | Notification alone does not resolve a finding |
| Monitoring with MSP review | Clients that need help interpreting matches | Relevance review, dated evidence, and an action recommendation | Review does not establish current compromise |
| Monitoring with agreed response | Clients delegating specified follow-up actions | Review plus explicitly authorized response tasks | Unspecified investigation remains outside scope |
Monitoring and notification keeps the handoff narrow, but it leaves investigation with the client. MSP review adds interpretation, but it requires staff time and a defensible evidence record. Agreed response creates clearer operational ownership, but only when the authorization and exclusions are written down.
Choose the scope your team can execute and your client can understand. Avoid a broad label such as managed protection when the actual deliverable is an automated notification.
Monitoring and notification
Specify the enrolled objects, recipient, notification method, and escalation route. Ask the buyer to identify who owns investigation after notification.
The advantage is a clear division of responsibility. The limitation is equally clear: an unanswered notification can leave the next action undecided. Record how your MSP handles that situation without promising an unagreed response service.
Monitoring with MSP review
Define what a technician examines before a finding reaches the client. Preserve the source, observation date, affected object, and evidence limits.
This scope supports a more useful conversation than forwarding an unexplained alert. Its cost calculation must also include investigation that ends with an inconclusive result. Unknown evidence still requires a documented outcome.
Monitoring with agreed response
Name the permitted actions and the conditions that trigger approval. Separate routine follow-up from incident investigation and recovery.
This scope gives the buyer a defined next step. It also requires permissions, an escalation owner, and a way to verify completion. A monitoring subscription by itself does not establish those arrangements.
Why dark web monitoring cost per client varies
Use these factors to structure your 2026 quote requests. Ask each supplier to answer against the same proposed client scope.
- Billing unit: Establish exactly what the supplier counts and how additions or removals affect the commitment.
- Contract allocation: Decide how your MSP assigns shared commitments across enrolled clients, including unused capacity.
- Review responsibility: Define whether your team forwards notifications or validates relevance and explains the evidence.
- Response boundary: Specify which follow-up actions are included and which require separate approval.
- Reporting requirements: Agree on the audience, evidence record, review cadence, and completion criteria.
- Coverage limits: Record excluded sources, unreadable evidence, and conditions the service cannot establish.
Do not treat a longer feature list as proof of a better fit. A feature only belongs in the comparison when it supports an agreed client outcome or a required delivery task.
Use your own delivery records to refine labor assumptions. Track review, client communication, and authorized follow-up separately so a quiet reporting period does not hide the work needed when a substantive finding arrives.
Keep the evidence separate from the sales claim
A breach-data match does not establish that an account is currently compromised. The source date, observation date, identity match, and available context determine what you can responsibly say.
Use an evidence record with distinct fields:
- Condition: What the source actually reports.
- Evidence: The source, relevant dates, and affected object.
- Boundary: What remains unverified or unreadable.
- Owner: Who can validate context and authorize action.
- Next choice: The review or response the buyer can approve.
For example, an illustrative finding could describe an address appearing in a breach-data source. The possible consequence is a reason to review account context and agreed controls. It is not proof that the person's current password is exposed or that an attacker has accessed the tenant.
Keep evidence states distinct. Observed, Inferred, Possible, Unknown, and Unreadable describe different claims; they are not a progression toward a confirmed incident. Coverage also needs its own record, including what was not assessed.
In a 2026 proposal, attach dates to the actual evidence rather than relying on the year printed on the document. A newly prepared proposal can contain an old observation.
Public observations and Microsoft 365 evidence answer different questions
Public-domain observations cannot establish Conditional Access coverage, application permissions, license assignments, Intune device state, or tenant sharing configuration. Those questions require appropriate internal evidence and authorization.
Customer-authorized read-only Microsoft 365 review concerns configuration and metadata. Keep mail, files, chats, documents, and prompts outside that evidence boundary. A dark web result does not fill a gap in tenant access or assessment coverage.
State the limit directly when the source cannot answer a question. Unread evidence stays unknown, not clean.
Turn the cost discussion into an agreed scope
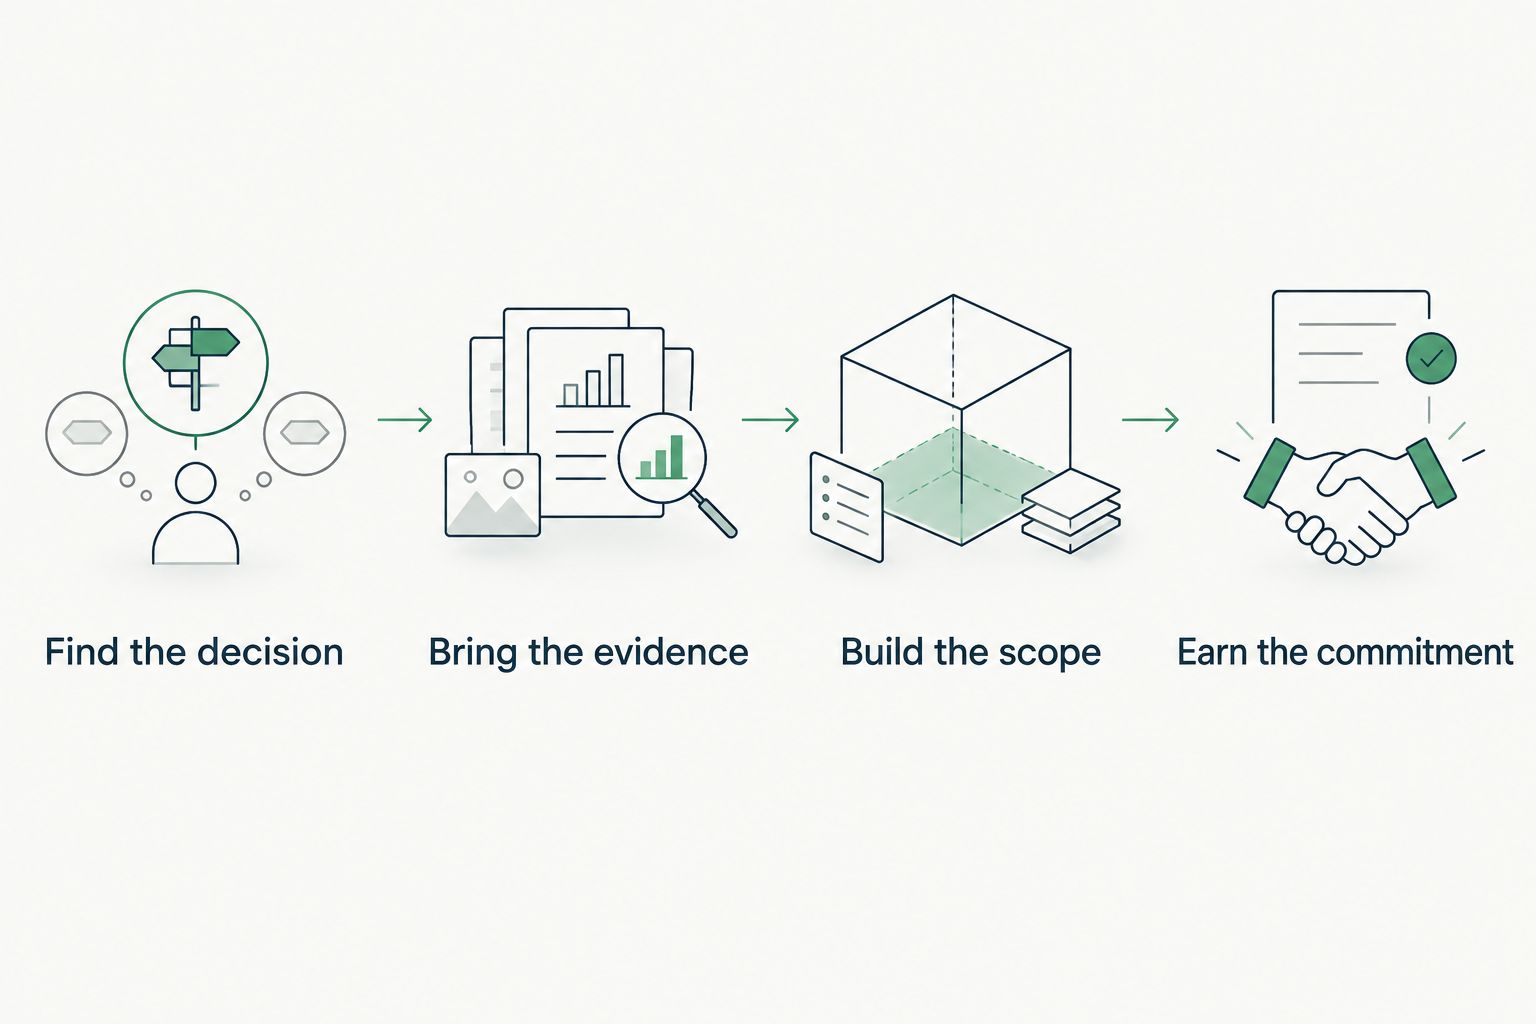
Use the SCOUTz Evidence-to-Agreement Framework to move from a finding to a decision. It is a conversation framework, not a proven sales-performance intervention.
Find the decision
Establish whether the buyer wants notification, interpretation, or delegated response. Identify who can approve the service and who will own follow-up inside the client's organization.
Illustrative dialogue: Your team would receive the notification under this scope. Would you rather own the review internally or have the MSP assess relevance before contacting you?
Bring the evidence
Show the dated observation and its limits. Explain why it deserves review without presenting it as a confirmed breach or a signal of buying intent.
Illustrative dialogue: This source associates the address with a breach-data record. It does not establish current account access. The proposed next step is to validate the account context with the authorized owner.
Build the scope
Compare the service choices in writing. Tie each responsibility to an owner and identify work requiring separate approval.
Illustrative dialogue: The reviewed service includes relevance assessment and an action recommendation. Incident investigation sits outside that recurring scope and needs separate authorization.
Earn the commitment
Ask for an explicit next action: validate enrollment, approve the review scope, or defer with an owner and review date. Preserve the buyer's choice.
Illustrative follow-up: Attached is the dated observation and proposed scope. Please confirm who owns account validation and whether you authorize the review. The agreement will record included work and exclusions.
Keep the proposal grounded in that exchange. An objection about cost can expose a scope mismatch: the buyer expects notification while your proposal includes review and response. Explain the difference without using speculative breach losses to pressure agreement.
Where prospect intelligence fits
SCOUTz is best for MSP owners and sales leaders preparing prospect conversations with dated cybersecurity evidence and account context. SCOUTz cybersecurity prospect intelligence supports preparation; evaluate an ongoing dark web monitoring service against its own delivery requirements.
SCOUTz, by RYTHMz, separates public-domain observations from customer-authorized Microsoft 365 evidence. The benefit is a defined evidence basis for discovery and proposals. The boundary is that prospect evidence does not establish buying intent, replace MSP judgment, or make the sale.
For a 2026 evaluation, confirm current scope and status before including any capability in a client commitment. The client-supplied October 15, 2026 reference identifies Microsoft 365 Review and Prospect Intelligence as Open Beta. Join Open Beta is the primary next step for MSPs evaluating SCOUTz cybersecurity prospect intelligence for meeting preparation.
FAQ
How much does dark web monitoring cost per client?
Calculate dark web monitoring cost per client from the allocated supplier commitment plus client-specific review, communication, and agreed response work. Compare quotes using the same coverage, billing period, and service responsibilities.
Should an MSP bill dark web monitoring per user or per client?
Choose a billing structure that clearly represents the coverage and service you agree to deliver. Keep your internal calculation tied to the supplier's actual billing unit and your delivery responsibilities.
Is dark web monitoring included in a Microsoft 365 security review?
Treat dark web monitoring and a Microsoft 365 security review as separate scopes unless your agreement explicitly combines them. A breach-data source and authorized tenant configuration evidence answer different questions.
Does a dark web match mean my client's account was hacked?
A dark web match does not confirm that your client's account was hacked. Preserve the source and dates, validate the identity and context, and state what the evidence cannot establish.
What should my MSP include in a monitoring proposal?
Include enrolled coverage, review responsibilities, notification routes, authorized actions, exclusions, and verification criteria. Name the owner of the next action so the service does not stop at an unexplained alert.
How do I compare an annual monitoring quote with a monthly quote?
Divide an annual commitment by 12 months to establish a comparable monthly obligation. Then account for differences in coverage, minimum commitments, included service work, and contract terms.
Can I promise that dark web monitoring prevents a breach?
Do not promise that dark web monitoring prevents a breach. Describe the evidence the service provides and the agreed review or response process without guaranteeing security or remediation.
One last thing
Write the verification step before you write the service promise. If the agreed action changes an account control, verify that control through the authorized source. Do not assume a historical breach-data record will disappear because the client completed the action.
That distinction makes the recurring review useful: preserve what was observed, record what changed, and identify what remains unknown. The client can then judge the work against an agreed outcome.