Dark web monitoring is worth it for small business clients when your MSP can connect a credible exposure alert to a defined investigation and response. It adds evidence about exposed data, but a breach-data match does not establish a compromised account, and the service needs an owner who can distinguish historical exposure from a current problem.
- Is dark web monitoring worth it for small business clients? Yes, when credible alerts lead to an owned response.
- A breach-data match establishes an exposure signal, not a confirmed account compromise or unresolved problem.
- Compare dark web monitoring, public-domain reviews and authorized Microsoft 365 assessments by their different jobs.
- SCOUTz cybersecurity prospect intelligence is best for MSPs preparing evidence-led conversations, rather than establishing compromise from exposure alerts.
Is dark web monitoring worth it for small business clients?
Yes, as an exposure-monitoring service with a response workflow. An alert feed alone does not tell your client whether an account remains active, whether a password changed or whether someone accessed the account.
For your 2026 service review, compare the evidence each review supplies before choosing a tool. The dark web monitoring tools for MSPs guide provides a separate starting point for evaluating that category.
| Review | Best for | Useful evidence | Main limitation |
|---|---|---|---|
| Dark web monitoring | Investigating reported data exposure | Matches between monitored identifiers and a provider's exposure sources | A match does not prove current credential validity or account compromise |
| Public-domain review | Preparing an external email and domain discussion | Publicly observable domain configuration, including published email-security records | Cannot establish internal tenant controls or account activity |
| Authorized Microsoft 365 review | Examining tenant configuration within agreed permissions | Customer-authorized configuration and metadata | Conclusions depend on permissions, licensing and readable sources |
These reviews answer different questions. Keep their findings separate rather than combining them into a single score that hides the source and coverage of each observation.
Why this matters
Your client needs to know what to do with a finding. A report showing an email address in breach data can justify checking the account's history and current controls; it cannot establish that the business has an active intruder.
The sales consequence is practical. If your proposal promises monitoring but leaves investigation ownership undefined, the buyer cannot tell what happens after an alert arrives.
Sell the service boundary alongside the evidence. State who reviews alerts, who authorizes account actions and what your MSP will document. That makes the proposal assessable without turning an exposure signal into a frightening claim.
Dark web monitoring: best for exposure follow-up
Dark web monitoring earns its place when a provider supplies enough context for your MSP to investigate a reported match. Evaluate the underlying sources, identifiers, available dates and explanation of what matched.
Preserve the distinctions between the provider's detection date, a reported incident date and your review date. A newly delivered alert does not necessarily describe a new exposure.
The benefit is a defined trigger for investigation. The limitation is visibility: a monitoring provider's covered sources do not represent every place exposed information might exist.
For a 2026 client review, record the disposition of the alert. Useful outcomes include an authorized account review, a documented historical exposure or an unresolved question awaiting evidence. An alert count alone does not demonstrate that a client received useful follow-up.
Avoid collecting or displaying exposed secrets as sales material. Give the buyer enough context to understand the observation without turning sensitive data into a presentation prop.
Public-domain reviews: best for external configuration context
A public-domain review gives your MSP evidence about externally observable configuration. A published DMARC policy requesting monitoring only is a condition you can discuss with the domain owner.
The possible consequence needs its boundary attached. A monitoring-only policy does not request rejection through that policy, but the observation does not establish successful spoofing, account compromise or an unintended configuration.
Ask who reviews the reports and whether monitoring-only remains the intended policy. That moves the conversation toward an owner and a decision.
The advantage is an external starting point without internal tenant evidence. The limitation is equally important: public observations cannot establish Conditional Access coverage, application permissions, license assignments, Intune device state or tenant sharing configuration.
Public observation and active probing also require different consideration. Agree on the assessment activity and authorization rather than treating a public domain as blanket permission to scan.
Microsoft 365 reviews: best for authorized tenant evidence
A customer-authorized Microsoft 365 review can add configuration evidence that public-domain observations cannot supply. Keep its permission scope and coverage visible in the report.
SCOUTz provides cybersecurity prospect intelligence for MSPs using dated domain evidence and customer-authorized Microsoft 365 reviews. The client-supplied product reference dated October 15, 2026 labels Microsoft 365 Review as Open Beta; its evidence boundary is read-only configuration and metadata, never mail, files, chats, documents or prompts.
The benefit is a more specific conversation about the tenant's observed configuration. The limitation is coverage: permission-limited, license-limited and unreadable evidence leave questions unanswered.
Keep evidence state separate from assessment coverage. An unread source belongs under “NOT ASSESSED THIS SCAN,” with the reason recorded. It does not support a clean result.
This distinction matters when an exposure alert leads to an authorized review. A configuration observation can inform the next action without proving that an exposed credential was used.
Why dark web monitoring value varies
The value depends on what your MSP can establish and deliver after an alert. Use these factors in your 2026 service design:
- Source context: Require an explanation of the matched identifier, available provenance and relevant dates. Preserve uncertainty when the provider cannot establish the original exposure date.
- Account relevance: Determine whether the identifier belongs to an active employee, former employee, alias or another account category before assigning work.
- Response ownership: Name the person responsible for triage, customer communication and authorization. Separate a recommendation from an action already completed.
- Assessment coverage: Record what the available evidence can establish. A public-domain review cannot fill gaps in internal tenant visibility.
- Evidence of follow-through: Define how your MSP records investigation, approved changes and verification. Keep the original observation attached to the outcome.
Choose the workflow before the alert feed. A service with clear ownership and honest limits is easier for a buyer to evaluate than a report built around alarming match totals.
Move from exposure evidence to an agreed next action
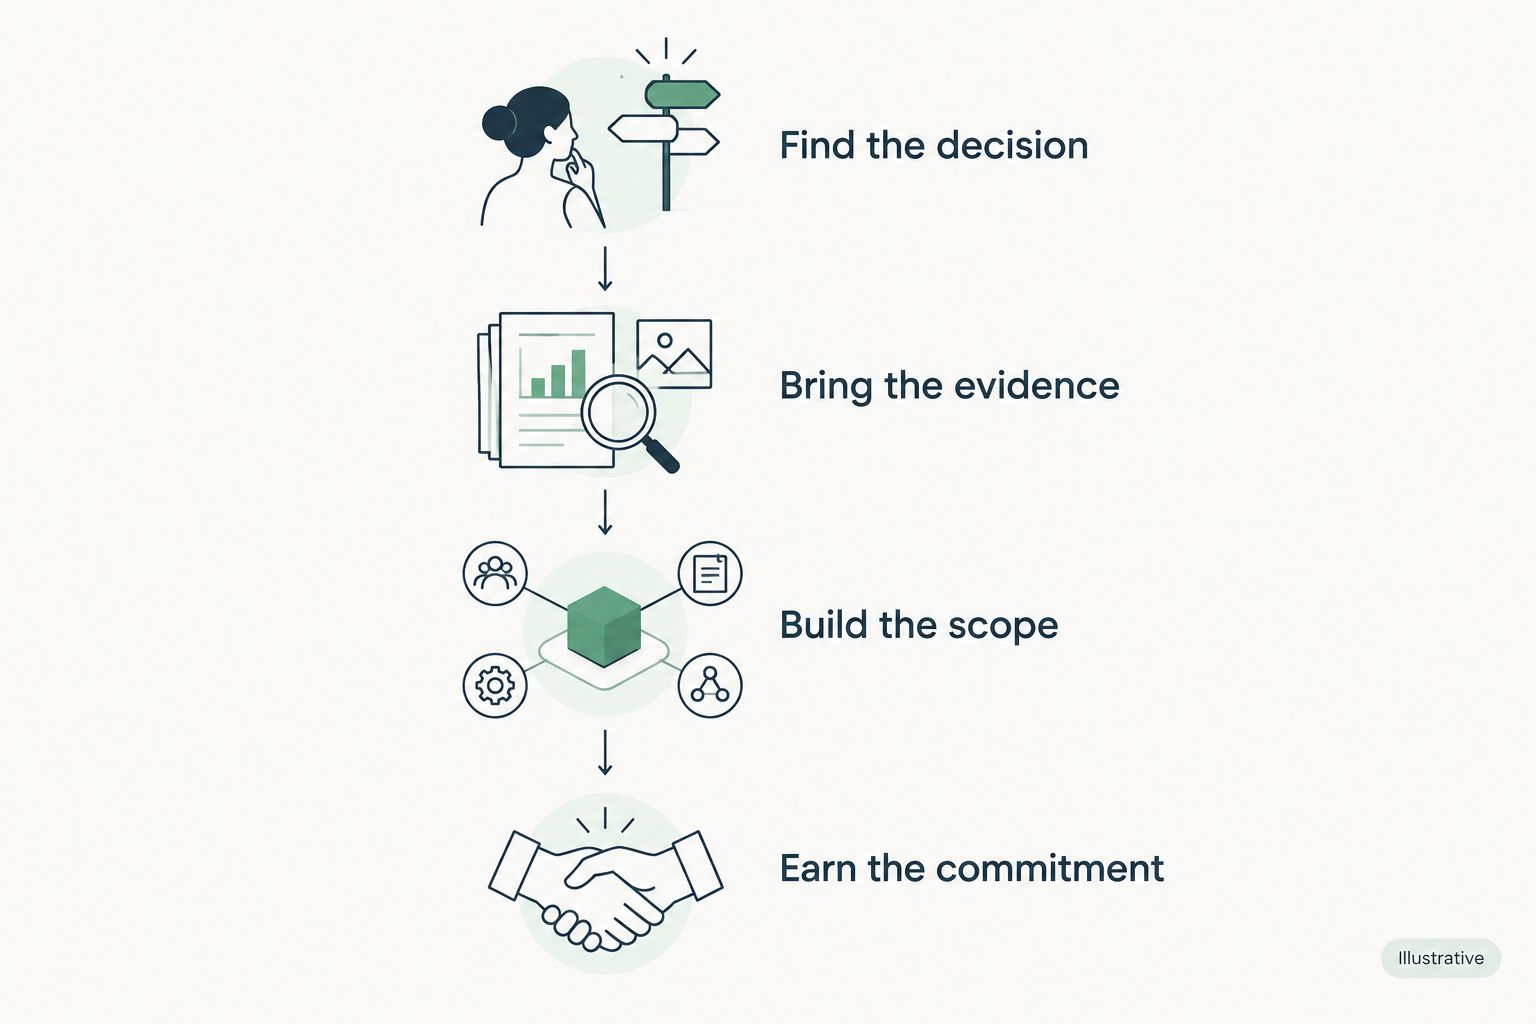
The SCOUTz Evidence-to-Agreement Framework gives an MSP a structure for this conversation: Find the decision, Bring the evidence, Build the scope, Earn the next commitment. It is a conversation framework, not a proven close-rate intervention.
Find the decision
Identify the decision the owner needs to make. Examples include authorizing an account review, assigning responsibility for exposure alerts or deciding whether ongoing monitoring belongs in the service agreement.
Keep the decision narrow enough to explain. A reported exposure does not automatically justify replacing the client's entire security stack.
Bring the evidence
Present the source, relevant dates, affected identifier and evidence limits. Separate what the provider observed from your MSP's interpretation.
For an exposure alert, describe the match as reported by the source. Leave current credential validity, account access and remediation status unknown unless additional evidence establishes them.
Build the scope
Describe the investigation and its deliverables before recommending a vendor. The scope should name the authorized evidence review, responsible owner, customer approvals and record of completion.
Keep the recommended outcome independent of the product choice. The MSP and client can choose a product, service, process, project or no additional work based on the evidence and their responsibilities.
Earn the next commitment
Ask for a specific, voluntary next action. That might be permission for a read-only tenant review, confirmation of the account owner or agreement to review a scoped proposal.
Record what the buyer actually agreed to. An email open, downloaded report or public business event does not establish buying intent.
These stages turn a technical observation into a decision process. They preserve the buyer's choice and leave responsibility for the relationship and sale with the MSP.
Use illustrative dialogue without inventing an incident
The following dialogue is illustrative. It describes a conversation pattern, not an actual customer finding or result.
MSP: “The monitoring source reports an email-address match in breach data. That does not establish that someone accessed your business account. We need to confirm who owns the account and what response has already happened.”
Client: “We already changed the password.”
MSP: “Then the next step is to document that action and decide whether any additional review is warranted. We should not present the original match as an unresolved password problem.”
Client: “Does this mean we need another security product?”
MSP: “The finding alone does not establish that. We can first agree on the outcome you need and review the relevant evidence with your authorization.”
The objection is useful information. It changes the scope from selling a presumed fix to establishing what remains unknown.
Keep follow-up equally specific. An illustrative message might read: “You confirmed that the password was changed. The reported exposure remains historical evidence; current account activity has not been assessed in this review. Please confirm whether you want an authorized review and who should approve its scope.”
That message records the boundary and requests a decision. It makes no claim about an incident, urgency or the prospect's willingness to buy.
Put the response boundary in the proposal
Your 2026 proposal should distinguish the monitoring service from investigation and remediation. Describe which work is included and which work requires separate approval without implying that every alert needs the same response.
Record the monitored identifiers, covered sources as described by the provider, triage owner and communication route. Specify how account ownership changes will be reflected in the service.
For investigation, name the evidence you intend to review and the permissions needed. Do not promise conclusions that the available configuration or metadata cannot support.
For verification, define what changed and how it will be checked. SCOUTz uses a rescan against a pinned baseline as proof of observed configuration change; that proof should stay attached to the relevant check and run date. A changed configuration does not establish that historical exposure disappeared from third-party collections.
For MSPs evaluating this evidence-led preparation workflow, the primary next step is Join Open Beta. Keep the product evaluation separate from your client's agreement to an assessment or service.
Does a dark web alert mean my client has been hacked?
A dark web alert does not establish that your client has been hacked. It reports a match within the monitoring provider's covered evidence sources, subject to that source's accuracy and context.
Investigate the affected identifier, relevant dates and current account ownership. Establish account compromise through evidence of compromise, rather than treating the existence of an exposure record as sufficient proof.
Should I include dark web monitoring in every client agreement?
Include dark web monitoring when its scope and response match the client's agreed needs. Define who handles alerts and how the service fits alongside existing account-security responsibilities.
A client can accept a scoped monitoring service or decline it. Document the decision without suggesting that a declined service proves indifference to security.
FAQ
Is dark web monitoring worth it for small business clients in 2026?
Dark web monitoring is worth it when credible exposure alerts lead to an owned investigation and response. Evaluate source context, account relevance and follow-through rather than alert totals alone.
Does a breach-data match prove an employee account is compromised?
A breach-data match does not prove an employee account is compromised. Keep the reported exposure separate from evidence about current credential validity, account access and response history.
Can a public-domain review tell me whether Microsoft 365 accounts are protected?
A public-domain review cannot establish internal Microsoft 365 account protections. Conditional Access coverage, application permissions and other tenant configuration require appropriately authorized internal evidence.
Should my MSP reset a password whenever monitoring finds an email address?
An email-address match alone does not determine the appropriate account action. Confirm the source context, account owner and response history, then follow the client's authorized response process.
Is a clean monitoring report proof that a business has no exposed data?
A report without matches is not proof that a business has no exposed data. Interpret the result within the provider's covered sources and monitored identifiers.
What should I show a small business owner after an exposure alert?
Show the reported observation, source, relevant dates, affected identifier and limits. Then identify the owner and offer a specific next choice without claiming an unverified incident.
Can I use a dark web finding to justify a security proposal?
A dark web finding can support a proposal when the proposed work addresses a documented question or agreed outcome. Keep the finding, unknowns, investigation scope and buyer's approval separate.
One last thing
A completed response can coexist with a continuing exposure record. Information remaining in a provider's collection does not, by itself, show that the client failed to act.
At your next review, put the original observation beside the authorized response and verification evidence. Explain what changed, what remains unknown and whether any further decision is needed. That gives the owner a useful account of the work instead of repeatedly presenting historical exposure as a fresh emergency.


