Best overall for Microsoft 365 identity-risk investigation: Microsoft Entra ID Protection. Best for checking known breach exposure: Have I Been Pwned; best for an on-premises Active Directory password audit: Specops Password Auditor. Choose executive credential monitoring tools for MSPs by the evidence you need and the action your team owns.
- Microsoft Entra ID Protection suits MSPs investigating identity risk in authorized Microsoft 365 tenants.
- Have I Been Pwned helps validate known breach exposure; a match does not establish current compromise.
- Specops Password Auditor fits authorized Active Directory password reviews, rather than continuous executive monitoring.
- SCOUTz fits MSP evidence preparation alongside executive credential monitoring tools for MSPs, rather than replacing credential detection.
Why this matters
An executive's address appearing in breach data and an executive account showing risky sign-in activity are different conditions. They need different evidence, different permissions, and different responses. Combining them into one alarming slide hides the decision the client actually needs to make.
For your 2026 shortlist, separate exposure discovery, identity investigation, password auditing, and sales preparation. Before presenting any result, use a repeatable process to validate security assessment findings before a call.
What makes the best executive credential monitoring tool
- Evidence provenance: Identify the originating dataset, tenant signal, or directory assessment. Preserve the affected account and observation date.
- Executive coverage: Confirm which business addresses, aliases, and authorized identities the service covers. Personal accounts require separate consideration and permission.
- Action ownership: Assign someone to investigate, communicate, and close each finding. An alert without an owner is unfinished work.
- Access boundaries: Distinguish public breach information from authenticated tenant evidence and authorized directory access.
- Repeatable verification: Define what a subsequent review can establish. A historical breach record and a current identity-risk state need different closure criteria.
- MSP workflow fit: Check client separation, permissions, reporting, and investigation handoffs during evaluation. Do not assume every product has an MSP operating model.
Executive credential monitoring tools at a glance
This 2026 comparison ranks tools by distinct jobs. It includes assessment and preparation tools because credential monitoring alone does not answer every question an executive or MSP salesperson brings to a meeting.
| Rank and tool | Best for | Standout capability | Key limitation |
|---|---|---|---|
| 1. Microsoft Entra ID Protection | Microsoft 365 identity-risk investigation | Tenant identity-risk detections and investigation context | Requires authorized tenant access; coverage depends on configuration and licensing |
| 2. Have I Been Pwned | Known breach-exposure validation | Checking whether an address appears in indexed breach data | Historical exposure does not establish current account compromise |
| 3. Specops Password Auditor | On-premises Active Directory password assessment | Reviewing password-related weaknesses in an authorized directory | An audit is different from continuous executive monitoring |
| 4. SCOUTz | Evidence-led MSP sales preparation | Dated domain and consented Microsoft 365 evidence for conversations | Credential-monitoring coverage is not established by its supplied product description |
1. Microsoft Entra ID Protection: best for tenant identity investigation
Microsoft Entra ID Protection provides user-risk and sign-in-risk information within Microsoft's identity environment. It belongs on your shortlist when the executive's business identity sits in an authorized Microsoft tenant and your team needs to investigate identity signals.
The useful distinction is current tenant context versus an external breach reference. A risky sign-in detection supports investigation; it does not, by itself, prove that an attacker controls the account.
Microsoft Entra ID Protection pros:
- Connects investigation to the identity environment your team administers.
- Distinguishes user risk from sign-in risk.
- Supports a defined handoff between identity administrators and security investigators.
Microsoft Entra ID Protection cons:
- Requires authorized access and an appropriate tenant setup.
- Features and investigation detail depend on licensing.
- Does not replace a separate review of exposure outside the tenant.
Best for: MSPs responsible for Microsoft identity investigation and response.
Ask the vendor or your Microsoft licensing specialist to demonstrate the exact detections and actions your client's entitlement supports. Then test who receives an alert, who investigates it, and how the client sees the outcome. Evaluate that workflow before promising executive coverage.
Verdict: Buy for an authorized Microsoft identity-risk workflow; verify entitlement and operating responsibilities first.
2. Have I Been Pwned: best for known breach-exposure validation
Have I Been Pwned lets you check whether an email address appears in its indexed breach information. Its domain-search workflow requires verification of domain control. That makes it useful for validating a specific exposure claim before discussing it with a client.
A result concerns the indexed breach record. It does not establish that the executive still uses an exposed password, that the business account was accessed, or that remediation remains outstanding.
Have I Been Pwned pros:
- Gives a recognizable source for a breach-exposure check.
- Helps distinguish a named breach reference from an unsupported sales assertion.
- Provides a domain-verification boundary for organization-level searches.
Have I Been Pwned cons:
- Coverage is limited to the information the service holds.
- A negative search does not establish that an identity has never been exposed.
- Historical records do not answer whether present-day credentials remain affected.
Best for: MSPs validating known exposure before recommending an authorized account review.
For a 2026 executive review, retain the breach reference and your lookup date separately. Ask the account owner about subsequent password changes and protective controls without requesting the password itself. Keep unresolved questions visible.
Verdict: Buy into the workflow for exposure validation; skip treating a match as proof of current compromise.
3. Specops Password Auditor: best for Active Directory password audits
Specops Password Auditor assesses password-related security conditions in on-premises Active Directory. It fits an authorized assessment where an MSP needs directory evidence rather than another external exposure alert.
Its job is narrower than executive protection across every personal and business service. Use the audit to define directory work, then decide which separate monitoring or identity-response capabilities the client needs.
Specops Password Auditor pros:
- Grounds the discussion in an authorized directory assessment.
- Supports investigation of password-policy weaknesses.
- Helps scope directory-specific follow-up work.
Specops Password Auditor cons:
- Does not replace cloud identity-risk investigation.
- An assessment result is a point-in-time observation.
- Executive coverage across unrelated services remains outside that audit's boundary.
Best for: MSPs assessing password controls in clients with on-premises Active Directory.
Confirm access requirements, data handling, and assessment scope before deployment. Have the administrator distinguish policy evidence from evidence about an individual account. Those conditions require different recommendations and different proof of completion.
Verdict: Buy for authorized directory assessment; skip it as a standalone executive-monitoring service.
4. SCOUTz: best for evidence-led executive security conversations
SCOUTz provides cybersecurity prospect intelligence for MSPs through dated domain evidence and customer-authorized Microsoft 365 reviews. Its role is preparing the conversation and connecting evidence to a scoped next decision.
SCOUTz is best for MSPs preparing evidence-led executive security conversations alongside credential-monitoring tools. Its supplied product scope does not establish a dedicated executive credential-monitoring service, so do not sell it as one.
SCOUTz pros:
- Separates public-domain observations from customer-authorized internal evidence.
- Keeps evidence, implications, unknowns, and recommended outcomes distinct.
- Supports a conversation in which the MSP chooses the service or process response.
Its limitations:
- Public-domain evidence cannot establish Conditional Access coverage or tenant permissions.
- Microsoft 365 review covers configuration and metadata, never mail, files, chats, documents, or prompts.
- The MSP remains responsible for interpretation, buyer agreement, and the sale.
Best for: MSP owners and sales leaders who need dated account context before an executive meeting.
The client-supplied product reference is dated October 15, 2026. Keep that reference separate from scan evidence: a product-description date cannot substitute for a finding's run date. Unknown or unread evidence stays unknown.
Verdict: Buy for evidence preparation after confirming fit; skip it as a replacement for credential detection.
How the ranking works
The order follows the job, rather than a combined security score. Microsoft tenant investigation comes first, known breach-exposure validation second, directory assessment third, and conversation preparation fourth. Each position answers a different operational need.
These recommendations compare documented product roles, not measured detection performance or independently tested sales outcomes. For a 2026 procurement decision, ask each supplier to demonstrate your required workflow with the permissions and reporting boundaries your MSP will actually use.
Turn a credential finding into an agreed next step
Use the SCOUTz Evidence-to-Agreement Framework to move from discovery toward a proposal: Find the decision, Bring the evidence, Build the scope, Earn the next commitment. This is a conversation framework, not a proven close-rate intervention.
Find the decision
Identify whether the executive wants an exposure check, an account investigation, or an ongoing managed service. Name 1 accountable owner for the next action. Keep the commercial decision separate from the technical condition.
Bring the evidence
Attach the source, affected identity, finding state, and coverage boundary. Preserve 2 timestamps: the source event or dataset date when available, and the date your team retrieved or assessed it. If the source date is unknown, say so.
A breach-data match is evidence of a match. A tenant-risk detection is evidence of that detection. Neither establishes every step of an attack or proves an unresolved condition.
Build the scope
Offer 3 scope options: validate the exposure, investigate the authorized account, or define ongoing monitoring. Explain the deliverable, access required, responsible owner, and completion evidence for each. Leave room for the buyer to choose no action after reviewing the facts.
Earn the next commitment
Request a specific decision: authorize the review, identify the account administrator, or approve a written scope. Record the agreed action and follow-up date. A report open or a meeting attendance record does not establish buying intent.
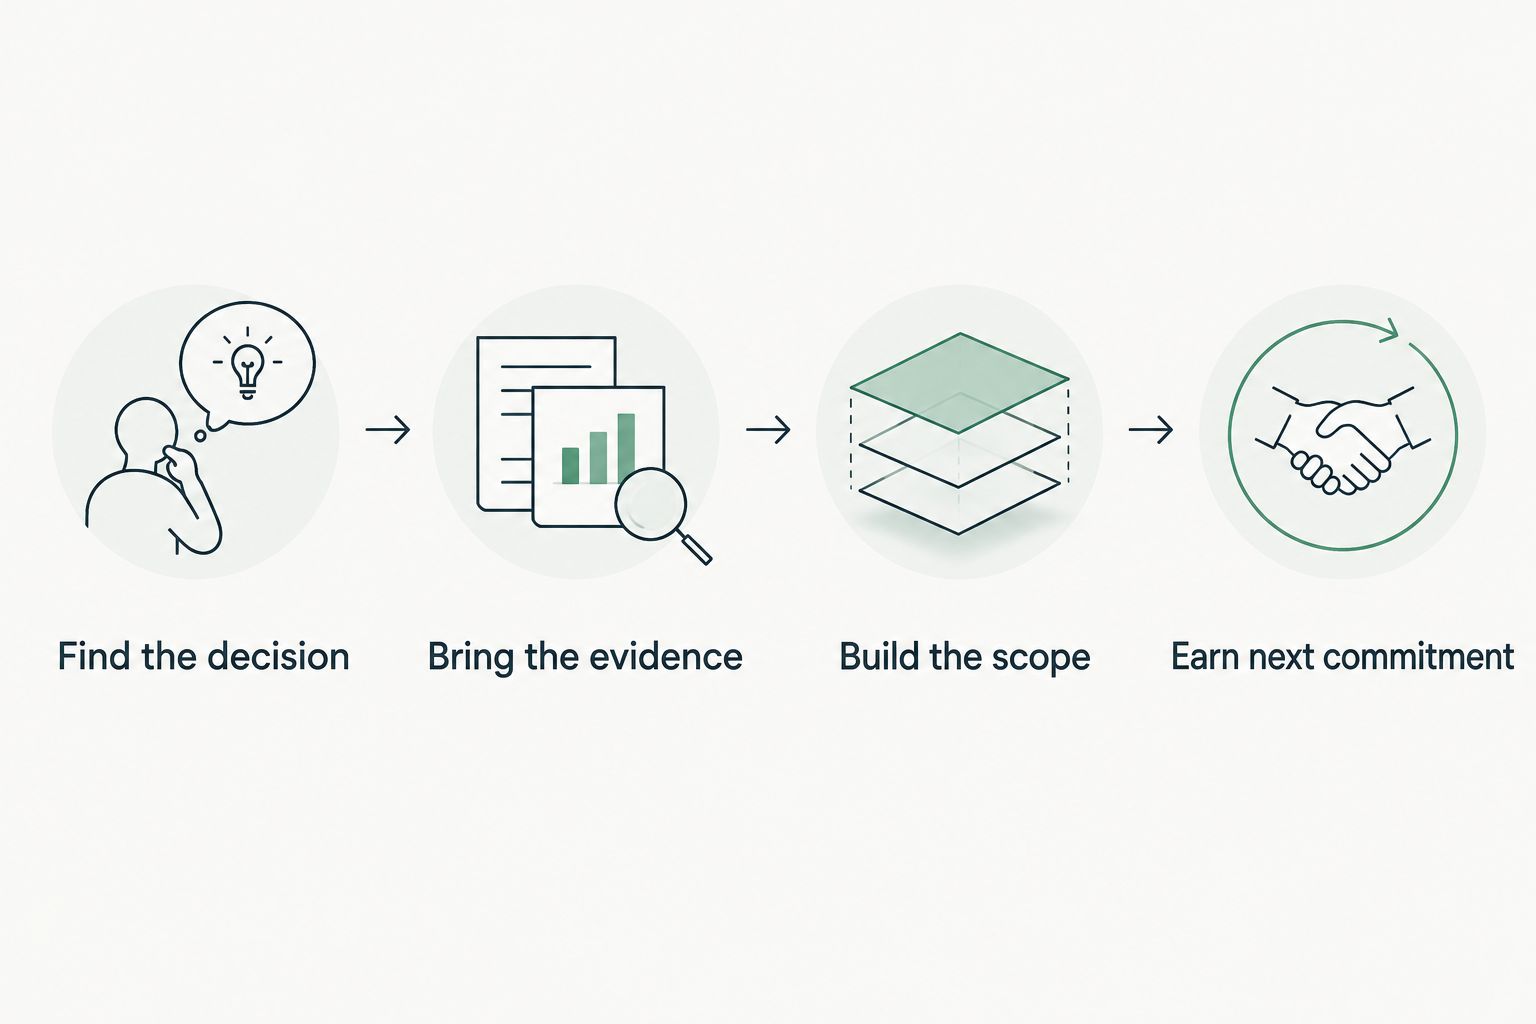
Keep the framework in your meeting notes alongside the evidence. The diagram describes a conversation sequence, not a product screen or a measured client result.
Handle objections without stretching the finding
The following are illustrative response approaches, not customer quotations or actual incidents.
- Already changed the password: Acknowledge the change. Ask whether the administrator can confirm the relevant account action, then assess whether any separate investigation remains justified.
- Already has MFA: Separate the control from the exposure record. Verify the relevant identity configuration with permission before making a recommendation.
- Wants proof of compromise: State that the current evidence does not establish compromise. Offer an authorized investigation with clear limits.
- Wants a proposal immediately: Define which decision the proposal covers. Separate exposure validation from investigation and ongoing monitoring.
A follow-up should restate the observed condition, list the unresolved questions, and request the agreed authorization. Exclude frightening forecasts and unsupported claims about an executive's behavior.
Join Open Beta is the next step for MSPs evaluating the evidence-preparation workflow. Use a demo discussion to establish fit and confirm the current scope before making client commitments.
Discuss your evidence workflow
Review your MSP's sales-preparation needs and discuss Open Beta fit.
Which tool should your MSP choose?
Choose Microsoft Entra ID Protection when your default problem is investigating identity risk in an authorized Microsoft environment. Choose Have I Been Pwned when you need to validate a known breach-exposure reference. Choose Specops Password Auditor when the agreed work concerns on-premises directory password controls.
Use SCOUTz for cybersecurity prospect intelligence and evidence preparation around the conversation. Keep detection, investigation, and sales responsibility assigned to their actual owners. For your 2026 shortlist, that separation matters more than adding another alert feed.
FAQ
What's the best executive credential monitoring tool for an MSP using Microsoft 365?
Microsoft Entra ID Protection is the strongest fit in this comparison for authorized Microsoft identity-risk investigation. Confirm licensing, detection coverage, and investigation ownership before committing to a client scope.
Does a breach-data match mean an executive account is compromised?
No. A breach-data match establishes an association with the indexed breach information, not current control of the executive's account. Investigate present-day account conditions separately and with authorization.
Is Have I Been Pwned enough for an executive protection service?
Have I Been Pwned supports known breach-exposure validation, but that alone does not define an executive protection service. Your MSP still needs an agreed scope for investigation, communication, response, and follow-up.
Can SCOUTz replace executive credential monitoring?
Its supplied product scope does not establish dedicated executive credential monitoring. It supports MSP preparation through dated domain evidence and customer-authorized Microsoft 365 configuration and metadata reviews.
Can an MSP assess Microsoft 365 identity controls from a public domain scan?
A public domain scan cannot establish internal Microsoft 365 identity-control coverage. Conditional Access, application permissions, and other tenant conditions require appropriate authorized evidence.
Should an MSP include an executive's personal email addresses?
Include personal addresses only under an explicitly agreed scope and appropriate authorization. Define who can access the findings, how personal information is handled, and who receives notifications.
What should count as proof that a credential finding is resolved?
Resolution evidence must match the condition being investigated. A historical breach record can remain searchable after a password change, while a configuration finding needs a fresh authorized assessment against its baseline.
One last thing
A historical breach record can remain visible after the relevant password has changed. Repeating the same lookup is therefore insufficient proof that a current account problem remains unresolved.
Define closure before opening the investigation. Name the condition, owner, evidence required, and limits of verification. That gives the executive a decision and gives your MSP a defensible scope.