Best overall approach for MSPs in 2026: choose identity, endpoint and email controls by their separate jobs. Best for prospect-meeting preparation: SCOUTz; best for Microsoft identity policy: Microsoft Entra ID; best for endpoint investigation: Microsoft Defender for Endpoint; best for Microsoft email protection: Microsoft Defender for Office 365.
- The best MSP tools for identity endpoint email security cover separate control layers; assessment evidence cannot replace protection.
- SCOUTz is best for MSPs preparing evidence-led prospect conversations, with public-domain and consented Microsoft 365 boundaries kept separate.
- Microsoft Entra ID handles identity policy; Microsoft Defender for Endpoint handles endpoint detection and response.
- Microsoft Defender for Office 365 addresses email threats; Microsoft Intune handles device management and compliance policies.
Why This Matters
A prospect can have security products and still lack an agreed answer about what those products cover. Your sales conversation needs evidence of the condition, the responsible owner and the decision required.
Start with 3 control layers: identity, endpoint and email. Treat device management as supporting enforcement and assessment as supporting understanding. Neither substitutes for the others.
SCOUTz is best for MSPs preparing cybersecurity prospect conversations with dated domain and customer-authorized Microsoft 365 evidence. It prepares the conversation. The relationship and the sale stay yours.
What Makes the Best MSP Security Tools
Use these criteria for your 2026 shortlist before comparing dashboards:
- Job fit: distinguish protection, investigation, device management and sales preparation.
- Evidence quality: keep the source, collection date, affected object and limits attached to findings.
- Enforcement scope: identify which users, devices, applications or messages a policy actually covers.
- Operating responsibility: name who reviews alerts, approves changes and handles exceptions.
- Access boundaries: distinguish public observations from authorized tenant evidence and endpoint telemetry.
- Verification: define what evidence will demonstrate the agreed outcome after work is complete.
A tool belongs on your shortlist when its job matches the service you can deliver. A finding count alone does not establish that fit.
MSP Security Tools at a Glance
The order below follows distinct use cases, starting with sales preparation. It is not a claim that an assessment platform provides stronger protection than an enforcement product.
| Tool | Best For | Standout Capability | Key Limitation |
|---|---|---|---|
| SCOUTz | Evidence-led prospect preparation | Dated domain and consented Microsoft 365 evidence | Read-only review does not enforce controls |
| Microsoft Entra ID | Identity and access policy | Conditional Access and authentication policy | Identity policy does not establish endpoint protection health |
| Microsoft Defender for Endpoint | Endpoint investigation and response | Endpoint detection and response | Device onboarding and operational response remain necessary |
| Microsoft Defender for Office 365 | Microsoft email-threat protection | Email-threat protection and investigation | Email controls do not establish complete identity coverage |
| Microsoft Intune | Device management and compliance | Device configuration and compliance policies | Device compliance is not proof of incident-free operation |
1. SCOUTz: Best MSP Tool for Prospect Evidence
SCOUTz, by RYTHMz, gives MSPs dated cybersecurity evidence and account context for discovery, proposals and review conversations. Public-domain observations and customer-authorized Microsoft 365 evidence have different boundaries.
The Microsoft 365 review is read-only and covers configuration and metadata. It does not read mail, files, chats, documents or prompts, and it makes no automatic configuration changes.
SCOUTz pros:
- Keeps the sales conversation tied to observed conditions rather than speculative breach losses.
- Supports a distinction between external observations and consented internal evidence.
- Uses rescans against a pinned baseline to support proof of change.
SCOUTz cons:
- Does not replace identity enforcement, endpoint protection or email filtering.
- Public-domain evidence cannot establish tenant Conditional Access coverage or Intune device state.
- Microsoft 365 Review and report experiences carry Open Beta status in the client-supplied October 15, 2026 product reference.
Best for: MSP owners and sales leaders who need evidence before proposing work.
Verdict: Buy for the evidence-preparation role only after validating the beta workflow against your requirements.
2. Microsoft Entra ID: Best MSP Tool for Identity Policy
Microsoft Entra ID manages identities and access to applications. Conditional Access lets administrators apply access requirements based on policy conditions; the effective result depends on configuration, scope and applicable licensing.
For an MSP, the useful question is whether the intended people and applications receive the intended controls. MFA registration alone does not establish enforcement.
Microsoft Entra ID pros:
- Provides identity and application-access policy in the Microsoft environment.
- Supports Conditional Access for defined access requirements.
- Supplies identity configuration and sign-in evidence for authorized investigation.
Microsoft Entra ID cons:
- Policy exclusions and scope require explicit review.
- Feature access depends on the tenant's licenses.
- Identity configuration alone cannot establish device protection or mailbox investigation coverage.
Best for: MSPs responsible for Microsoft identity controls and access-policy decisions.
Verdict: Buy when identity enforcement is in scope; verify policy coverage before calling the tenant protected.
3. Microsoft Defender for Endpoint: Best for Endpoint Investigation
Microsoft Defender for Endpoint provides endpoint detection and response capabilities. It supports investigation of activity on onboarded devices and response actions within its supported environment.
For a 2026 service proposal, separate the existence of a subscription from working coverage. Your review should identify the devices in scope, their onboarding state and the team responsible for responding.
Microsoft Defender for Endpoint pros:
- Supplies endpoint telemetry for security investigation.
- Supports detection and response on covered devices.
- Gives an endpoint operations team evidence beyond a software inventory entry.
Microsoft Defender for Endpoint cons:
- Unmanaged or unonboarded devices remain outside the intended coverage.
- Alerts still require an accountable response process.
- Endpoint evidence does not establish email-authentication policy or tenant-wide access enforcement.
Best for: MSPs delivering endpoint security operations with an identified response owner.
Verdict: Buy for endpoint detection and response when onboarding, monitoring and escalation are part of the service.
4. Microsoft Defender for Office 365: Best for Microsoft Email Threats
Microsoft Defender for Office 365 provides protection and investigation capabilities for threats involving Microsoft email and collaboration services. Exact capabilities depend on the selected plan and configuration.
Keep message protection separate from domain authentication. SPF, DKIM and DMARC answer different questions from malicious-link handling or message investigation.
Microsoft Defender for Office 365 pros:
- Addresses email threats within the Microsoft environment.
- Supports investigation of suspicious email activity.
- Complements identity controls rather than asking one control layer to do every job.
Microsoft Defender for Office 365 cons:
- Policy configuration and coverage require validation.
- Domain-authentication work remains a separate responsibility.
- An email-protection finding cannot establish whether an account has been compromised.
Best for: MSPs managing Microsoft email-threat controls and investigation workflows.
Verdict: Buy for email protection when the proposal includes policy ownership and an investigation process.
5. Microsoft Intune: Best for Device Compliance Management
Microsoft Intune manages devices, applications and configuration policies. Device compliance policies can contribute device-state information to access decisions when the relevant services are configured together.
That makes Intune a management layer with security consequences. A compliant device status is not a declaration that the device has never experienced malicious activity.
Microsoft Intune pros:
- Provides a place to manage device configuration policies.
- Supports device compliance requirements.
- Helps connect device-management responsibilities with access-policy decisions.
Microsoft Intune cons:
- Enrollment and supported management capabilities determine coverage.
- Compliance depends on the rules you define and the evidence available.
- Device management does not replace endpoint detection and response.
Best for: MSPs standardizing managed-device configuration and compliance requirements.
Verdict: Buy for device management when enrollment, exceptions and ongoing policy ownership are included.
Turn the Shortlist Into an Agreed Scope
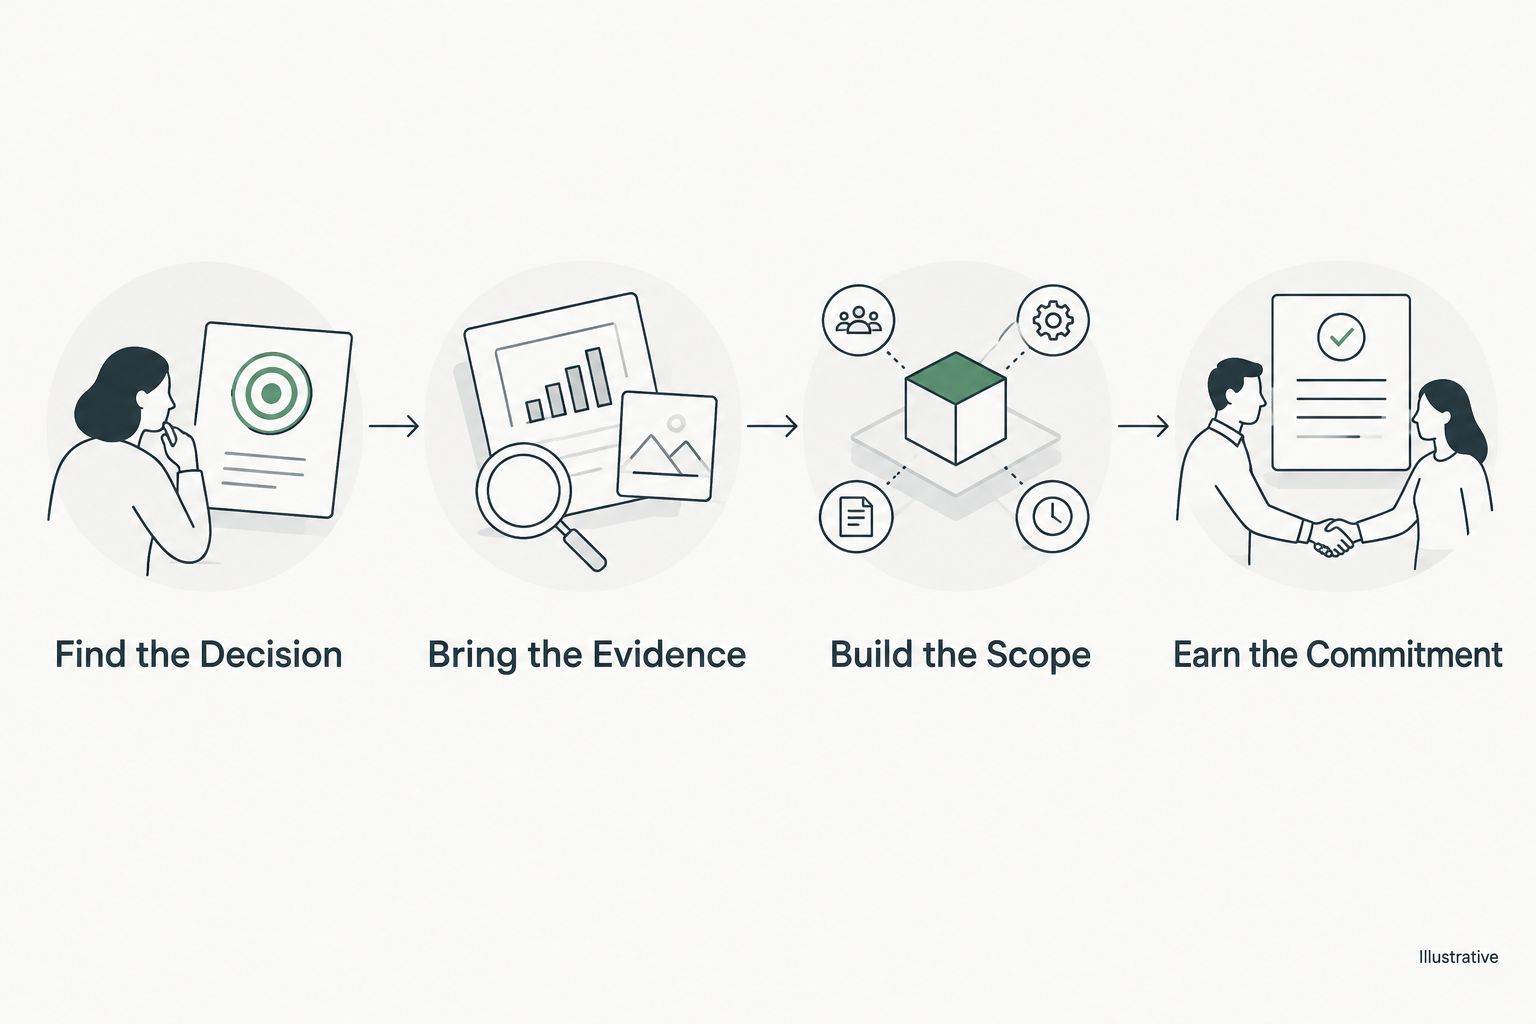
A product comparison should end with a decision the prospect understands. Use the SCOUTz Evidence-to-Agreement Framework: Find the decision, Bring the evidence, Build the scope, Earn the next commitment.
This is a conversation framework, not a validated close-rate intervention. In 2026, keep the same standard for every vendor: distinguish what the evidence establishes from what still needs authorization or investigation.
Find the Decision
Identify the business decision before presenting the findings. The prospect might need to choose between a focused configuration review and a broader managed-security engagement.
Write down the decision owner and the required approval. A technical contact's interest does not establish purchasing authority or buying intent.
Bring the Evidence
Attach the check, source, run date, affected object and coverage boundary. For internal identity evidence, the principle behind Okta access control evidence is the same: a claim about access controls needs evidence from the relevant identity system, collected with appropriate authorization.
Public DNS cannot establish Conditional Access coverage. An authorized tenant review can assess the configuration it can read; permission-limited evidence must retain that limit.
Before presenting the packet, validate the security assessment findings before a call. Remove stale claims, preserve unresolved unknowns and assign a practitioner to sign off.
Build the Scope
Offer 2 scope choices with different outcomes. Keep product selection separate from the condition being addressed.
| Scope Choice | Evidence Required | Agreed Outcome | Boundary |
|---|---|---|---|
| Focused identity review | Authorized policy and coverage evidence | Document intended enforcement and exceptions | Does not include endpoint response operations |
| Managed endpoint service | Device inventory, onboarding evidence and response requirements | Establish covered devices and response ownership | Does not resolve email-authentication policy |
A prospect can choose a service, a project, a process change or no action. The evidence should make those choices clearer.
Earn the Next Commitment
Ask for the next authorized action, its owner and the acceptance condition. Do not turn an email open or a report download into agreement.
Illustrative follow-up wording: Please confirm whether you want the focused identity review or the endpoint-service scoping session. The attached evidence describes the observed condition and collection limits. No configuration change is authorized by this message.
These 4 decision steps connect discovery to a proposal without promising a sale.
How the Ranking Works
These recommendations compare jobs, evidence boundaries and operating responsibilities. They are not benchmark-test results or a claim that one vendor wins across every category.
For your 2026 evaluation, ask each supplier to demonstrate the workflow you intend to sell. Require an example of incomplete coverage as well as a successful result. Unknown and unreadable evidence must remain visible.
Which MSP Security Tools Should You Choose?
Choose Microsoft Entra ID for identity policy, Microsoft Defender for Endpoint for endpoint response, Microsoft Defender for Office 365 for email-threat protection and Microsoft Intune for device management. Add the evidence-preparation layer when your prospect conversations lack dated, reviewable account context.
Join Open Beta is the primary next step for MSPs evaluating that preparation workflow. A demo can establish whether the current beta scope fits your sales process before you commit.
Evaluate the Evidence Workflow
Discuss public-domain evidence, consented Microsoft 365 reviews and the current beta scope.
FAQ
What's the best MSP tool for identity security?
Microsoft Entra ID is the identity-policy pick in this shortlist for MSPs managing Microsoft environments. Validate Conditional Access scope, exclusions and licensing before making a coverage claim.
Is endpoint protection the same as device management?
No. Microsoft Defender for Endpoint supports endpoint detection and response, while Microsoft Intune manages devices and configuration. The services address different operating responsibilities.
Can SCOUTz replace endpoint or email security?
No. SCOUTz prepares MSP conversations with dated evidence and account context. Enforcement and ongoing security operations remain separate responsibilities.
Can a public domain review show whether MFA is enforced?
No. Public-domain evidence cannot establish tenant MFA or Conditional Access coverage. That requires appropriately authorized internal evidence and review of the relevant policy scope.
Does a monitoring-only DMARC policy mean a company was breached?
No. A monitoring-only DMARC policy describes a published authentication-policy choice, not a confirmed compromise. Clarify the intended policy, reporting owner and authorized next action.
What should an MSP do when evidence cannot be read?
Record the unread source and the coverage limit explicitly. Permission-limited, license-limited or unassessed evidence must not be reported as a clean result.
How should MSPs compare security-tool costs?
Compare the licensed scope, implementation work and ongoing operating responsibilities using current supplier terms. A subscription comparison alone leaves onboarding, exception handling and response ownership unresolved.
One Last Thing
A green device-compliance result and a monitoring-only DMARC record can both be accurately reported. Neither answers whether your proposed service addresses the prospect's actual decision.
Pin the baseline before work begins. Then agree on the evidence that will demonstrate the outcome. That turns a security-tool recommendation into a scope you can verify.


