Best overall for DNSSEC diagnosis: DNSViz. Best for scheduled monitoring workflows: Zabbix. Best for command-line validation: BIND delv. The best MSP tools for monitoring DNSSEC and DNS security in 2026 serve different jobs: diagnosing trust-chain failures, detecting changes, and preparing evidence for a client decision.
- The best MSP tools for monitoring DNSSEC and DNS security separate validation diagnosis from recurring alerts.
- DNSViz is the default for visual DNSSEC diagnosis; Zabbix supports scheduled monitoring workflows.
- BIND delv helps practitioners investigate validation; Zonemaster checks broader delegation and nameserver behavior.
- SCOUTz is best for MSP prospect preparation using dated cybersecurity evidence, not a substitute for operational DNS monitoring.
Why this matters
A DNS answer can resolve successfully without proving that DNSSEC validation succeeded. An unsigned domain and a signed domain with a broken chain also need different responses. Treating both as the same security finding produces weak advice.
Your 2026 shortlist should separate three requirements: what you can observe, what needs specialist interpretation, and who receives an alert. For the customer-facing explanation, use the guide to explaining DNSSEC validation failures to a client.
SCOUTz is best for MSP prospect intelligence and sales preparation using dated evidence. DNSSEC-specific operational coverage still needs its own validation and monitoring workflow.
What makes the best DNSSEC and DNS security tools
- Validation accuracy: Distinguish secure, insecure, bogus, and indeterminate outcomes. A lookup result alone does not establish validation.
- Diagnostic depth: Show the relevant delegation, DS, DNSKEY, and signature evidence rather than a single unexplained status.
- Monitoring ownership: Define the schedule, alert destination, escalation owner, and recovery condition. A manual diagnostic page is not an alerting service.
- Evidence quality: Retain the queried name, record type, resolver or authoritative source, observation time, and limits.
- Client relevance: Explain the affected service and next verification step without claiming compromise or an unresolved problem from an isolated observation.
These criteria rank tools by job fit. No single entry replaces authoritative DNS administration, resolver validation, operational monitoring, and MSP judgment.
DNSSEC and DNS security tools at a glance
| Tool | Best for | Standout capability | Key limitation |
|---|---|---|---|
| DNSViz | Visual DNSSEC diagnosis | Graphical analysis of DNSSEC authentication relationships | A diagnostic run does not establish recurring alert coverage |
| Zonemaster | Delegation and nameserver review | Structured tests across DNS delegation and server behavior | Findings need technical interpretation and operational follow-up |
| BIND delv | Command-line validation troubleshooting | DNS lookups with DNSSEC validation and diagnostic output | Requires command-line skill and separate monitoring automation |
| Zabbix | Scheduled operational checks | Monitoring, triggers, and alert workflows | DNSSEC-specific checks require deliberate implementation |
| SCOUTz | Evidence-led prospect preparation | Dated public-domain evidence and account context | Not presented here as a dedicated DNSSEC monitoring service |
The 2026 default is DNSViz for investigation, paired with your operational monitoring system for recurrence. Add the other tools where their specific role fits your service.
1. DNSViz: best DNSSEC tool for visual diagnosis
DNSViz analyzes DNSSEC authentication relationships and displays them graphically. That makes it useful when you need to understand where a signed delegation or validation chain breaks, rather than simply recording that a lookup failed.
Use DNSViz when an engineer needs an explainable view of DS records, DNSKEY records, and signatures. Preserve the analysis time and affected name with the result. The output describes the analysis performed, not every resolver's experience indefinitely.
DNSViz pros:
- Visible relationships: Connect delegation and signing evidence in a graphical view.
- Focused diagnosis: Investigate DNSSEC authentication rather than treating every DNS error alike.
- Useful handoff: Give the DNS administrator concrete evidence to inspect.
DNSViz cons:
- Operational gap: A diagnostic run does not create an alert schedule or escalation policy.
- Interpretation burden: Your practitioner still needs to explain the failure and confirm its service impact.
Best for: Engineers investigating a suspected DNSSEC chain problem before recommending a change.
Verdict: Buy for visual diagnosis. Treat this as a tool-selection recommendation, not a claim about commercial terms.
2. Zonemaster: best DNS security tool for delegation review
Zonemaster tests DNS infrastructure across delegation, nameserver behavior, and DNSSEC-related conditions. It fits investigations where the problem extends beyond signing into the way a domain is delegated or served.
Use Zonemaster to broaden the question from whether validation succeeds to whether the delegation and authoritative servers behave as expected. Keep the individual test output. A summary status without its underlying condition is a poor basis for a customer-facing recommendation.
Zonemaster pros:
- Broader scope: Review delegation and authoritative DNS behavior alongside DNSSEC.
- Structured findings: Use named test results to support an engineering handoff.
- Cross-check value: Compare its observations with a separate validation investigation.
Zonemaster cons:
- Technical output: Test findings need interpretation before they become business recommendations.
- Workflow boundary: Testing does not assign an owner or verify that a later change fixed the condition.
Best for: MSP technicians reviewing a domain's delegation and nameserver configuration.
Verdict: Buy for delegation review. Keep operational alerting and change approval as separate responsibilities.
3. BIND delv: best DNSSEC tool for command-line investigation
BIND delv performs DNS lookups with DNSSEC validation. Its diagnostic options help practitioners examine validation behavior from a command-line environment.
Use delv when you need a reproducible query and retained output for an incident record or change review. Record the command, query target, resolver configuration, and execution time. Different resolver paths and cached data can produce different observations.
BIND delv pros:
- Reproducible queries: Preserve the command alongside its output.
- Validation focus: Investigate DNSSEC validation rather than relying only on whether an answer appeared.
- Scriptable operation: Incorporate command execution into an MSP-controlled workflow.
BIND delv cons:
- Practitioner requirement: Output needs DNS and DNSSEC knowledge.
- Automation responsibility: Your team must implement scheduling, result handling, and alerts if needed.
Best for: Technical teams that need repeatable validation diagnostics and control over query execution.
Verdict: Buy for command-line troubleshooting. Do not describe a saved command as a complete monitoring service.
4. Zabbix: best monitoring platform for scheduled DNS checks
Zabbix provides monitoring, triggers, and alert workflows. It belongs on this list as the operational layer where an MSP can implement recurring DNS checks and route actionable alerts.
A basic DNS availability check is not proof of DNSSEC validation. Define the exact condition your implementation tests, then test the trigger and recovery behavior. If you need DNSSEC-specific interpretation, supply a suitable check and preserve its diagnostic output.
Zabbix pros:
- Recurring execution: Place checks within an established monitoring schedule.
- Alert routing: Connect detected conditions to operational notifications.
- Recovery handling: Define when a monitored condition returns to its expected state.
Zabbix cons:
- Implementation work: DNSSEC validation logic is not established merely by adding a DNS lookup.
- Maintenance ownership: Scripts, dependencies, thresholds, and notification paths need ongoing care.
Best for: MSP operations teams prepared to own and test their monitoring implementation.
Verdict: Buy for scheduled monitoring workflows. Pair Zabbix with diagnostic evidence rather than relying on a generic up-or-down result.
5. SCOUTz: best DNS security companion for prospect preparation
SCOUTz provides cybersecurity prospect intelligence for MSPs through dated public-domain evidence and customer-authorized Microsoft 365 reviews. Its role is preparing an informed conversation and an agreed next action.
The client-supplied product reference dated October 15, 2026 identifies Domain Review as an established product and Microsoft 365 Review as Open Beta. That reference does not establish a specific DNSSEC collector, alert schedule, or continuous DNSSEC monitoring capability. Verify the actual report coverage before including DNSSEC in a proposal.
SCOUTz pros:
- Conversation context: Connect dated observations to discovery and scope.
- Evidence boundaries: Separate public-domain observations from consented internal evidence.
- Sales responsibility: Keep the relationship, recommendation, and sale with the MSP.
SCOUTz cons:
- Monitoring boundary: This article does not establish dedicated DNSSEC monitoring coverage.
- Access boundary: Public-domain review cannot establish internal Microsoft 365 configuration.
- Interpretation requirement: An observation does not establish compromise, buying intent, or a currently unresolved problem.
Best for: MSP owners and sales leaders preparing evidence-led prospect conversations.
Verdict: Buy for prospect preparation. Select operational DNS monitoring separately and confirm assessment coverage before promising deliverables.
How this ranking works
The ranking prioritizes validation accuracy and diagnostic clarity first, then operational ownership and customer-facing evidence. It compares documented tool functions and the supplied product scope, not measured performance or a hands-on benchmark.
For a 2026 selection, demonstrate your actual workflow before committing: run a diagnostic, preserve the result, route a test alert, and show how someone confirms recovery. A feature description does not prove that your implementation works.
Turn DNS evidence into an agreed next action
Use the SCOUTz Evidence-to-Agreement Framework to move from a technical observation to a buyer-approved scope. This is a conversation framework, not a proven close-rate intervention.
Find the decision
Name the decision before presenting findings: approve further investigation, authorize a DNS change, or accept the present configuration. Assign 1 named owner for the next action as a practical workflow rule.
Bring the evidence
Retain the check name, affected domain, source, and run date. For a disputed result, use 2 resolver viewpoints as a recommended cross-check, while recognizing that different caches and paths can explain different answers.
Separate evidence state from coverage. Unknown or unreadable evidence remains unknown or unreadable. It is not a clean result. Public DNS evidence also says nothing about Conditional Access coverage or application permissions inside a Microsoft 365 tenant.
Build the scope
Separate investigation from remediation. An investigation scope reproduces the observation and identifies the responsible administrator; a remediation scope defines the approved change, rollback approach, and validation outcome.
Keep condition, consequence, and vendor choice separate. An absent DNSSEC chain does not prove a breach or automatically require a change without reviewing the domain's requirements and ownership.
Earn the commitment
Offer a specific next choice and preserve buyer control. Retain 1 pinned baseline for the agreed verification, with the original observation and subsequent rescan clearly separated.
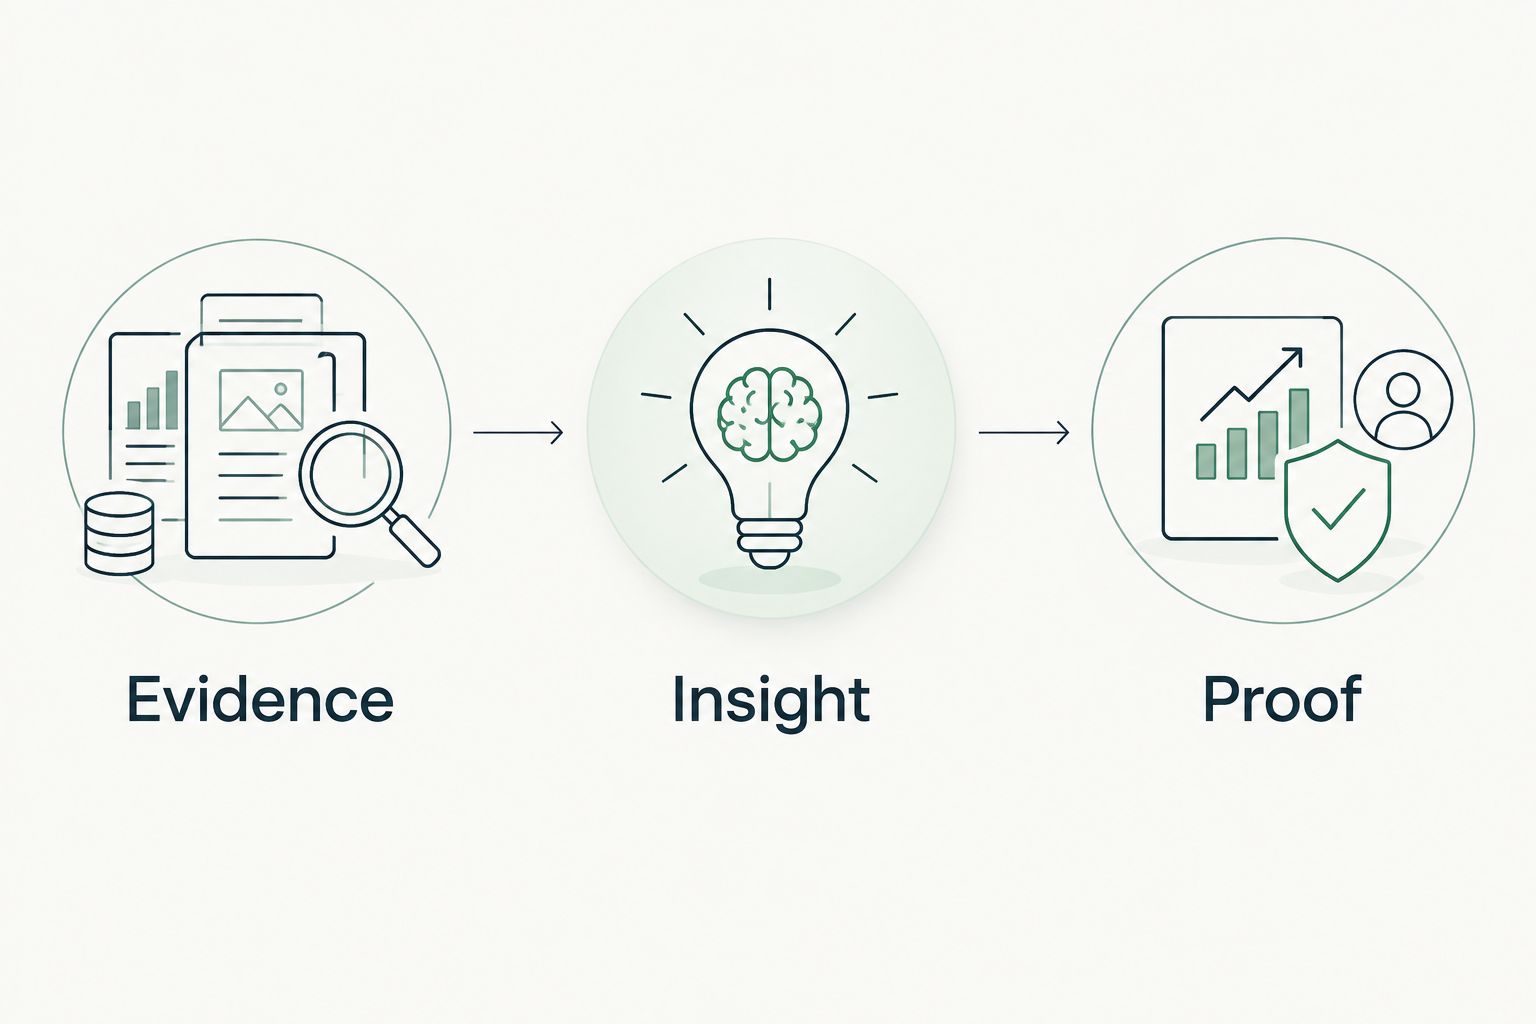
The evidence sequence is simple:
- Evidence: What ran, against which object, and when.
- Insight: What the observation means within its limits.
- Proof: What changed when checked against the pinned baseline.
Illustrative dialogue, not a customer quote: The MSP explains that the recorded validation attempt failed, identifies its date and resolver, and asks permission to reproduce it with the DNS administrator. The buyer chooses whether to authorize that investigation. No outage, compromise, or financial loss is assumed.
Illustrative objection handling: If the buyer says the website works, acknowledge that observation. Explain that availability from the buyer's current resolver does not settle the separate validation question. Offer a bounded verification task rather than arguing for an immediate project.
Illustrative follow-up script: Summarize the observed condition, attach the dated evidence, identify the unknowns, and request approval for the agreed investigation. State who owns the next action and what result will close it.
For prospect preparation, make Join Open Beta the primary next step. Use a demo conversation to discuss fit and confirm the coverage your proposed workflow requires.
Review your evidence workflow
Discuss prospect preparation, review boundaries, and Join Open Beta with the team.
Which DNSSEC and DNS security tools should you choose?
Choose DNSViz first if your immediate task is explaining a DNSSEC validation problem. Choose Zabbix when your immediate task is recurring checks and alert ownership. Add Zonemaster for delegation review or BIND delv for repeatable command-line investigation.
For your 2026 service design, write these as separate deliverables. Diagnosis identifies a condition; monitoring watches a defined condition; prospect preparation helps the buyer decide what to authorize. Combining their names does not combine their coverage.
FAQ
What's the best MSP tool for diagnosing DNSSEC problems?
DNSViz is the default recommendation here for visual DNSSEC diagnosis. Use its authentication analysis to investigate the affected chain, then retain the analysis time and domain with the result.
Is DNSViz a replacement for continuous DNS monitoring?
A DNSViz diagnostic run does not establish continuous monitoring. Recurring checks need a schedule, an alert destination, an owner, and a defined recovery condition.
Can Zabbix monitor DNSSEC validation?
Zabbix can support a monitoring workflow around a suitably implemented DNSSEC check. A generic DNS lookup alone does not establish validation coverage; test the check, trigger, and recovery behavior.
Is BIND delv better than a normal DNS lookup?
BIND delv is better suited to investigating DNSSEC validation than a lookup that only demonstrates an answer was returned. Preserve the command, resolver configuration, output, and execution time.
Does an unsigned domain mean a client has been breached?
An unsigned domain does not establish a breach. It describes a signing condition that needs context, ownership, and a decision about the intended configuration.
Can a public DNS review assess Microsoft 365 security?
A public DNS review cannot establish internal Microsoft 365 controls. Conditional Access, application permissions, license assignments, device state, and tenant sharing settings require appropriate authorized evidence.
What should an MSP keep as proof that a DNSSEC issue was fixed?
Keep the original dated observation and a later verification against a pinned baseline. Record the affected name, check, source, approved change, and remaining unknowns so the conclusion stays within the evidence.
One last thing
Successful resolution and successful validation are different outcomes. Before you sell DNSSEC monitoring, make your team demonstrate both the failure alert and the recovery evidence. That exercise turns a tool choice into a defined service responsibility.


