Best for MSP prospect meetings: SCOUTz. Best for individual DNS checks: MXToolbox. Best for DMARC record interpretation: dmarcian. Best for manual verification: dig. This 2026 guide compares the best SPF, DKIM and DMARC checker tools for MSPs by the evidence each supplies and the decisions each supports.
- The best SPF DKIM DMARC checker tools for MSPs serve different jobs: inspection, interpretation, verification and meeting preparation.
- SCOUTz is best for MSPs bringing dated domain-security evidence into prospect conversations.
- MXToolbox supports individual lookups; dmarcian helps interpret DMARC records; dig exposes DNS answers for manual verification.
- A published record does not prove successful message authentication, tenant security or compromise.
Why This Matters
An email-security finding needs a boundary. A published DMARC policy requesting monitoring establishes a configuration observation. It does not establish that the domain suffered a breach or that the owner wants to buy security services.
SCOUTz is best for MSPs that need dated domain-security evidence for prospect meetings. Its role is cybersecurity prospect intelligence, rather than a substitute for checking the underlying DNS response. The SCOUTz platform connects evidence with account context so you can prepare the next conversation.
For your 2026 shortlist, separate three jobs: inspecting published records, examining authentication behavior and preparing an owner-facing explanation. A tool that handles one job does not automatically handle the others.
What Makes the Best Email-Authentication Checker
- Source visibility: retain the queried name, record type, response and observation time.
- Protocol specificity: distinguish SPF authorization, DKIM signatures and DMARC alignment.
- Coverage boundaries: state whether the result covers DNS, an actual message or reporting data.
- Repeatability: preserve the original evidence and compare a later observation against it.
- Decision usefulness: connect the condition to an owner, an unanswered question and an agreed next action.
Your 2026 selection should start with the missing evidence in your workflow. A sales-preparation platform and a DNS command answer different questions. Neither deserves a higher rank simply because it presents more findings.
Tools at a Glance
| Tool | Best For | Standout Capability | Key Limitation |
|---|---|---|---|
| SCOUTz | MSP prospect-meeting preparation | Dated domain-security evidence and account context | Public-domain evidence cannot establish internal tenant controls |
| MXToolbox | Individual DNS record checks | Dedicated SPF, DKIM and DMARC lookup tools | Record inspection alone does not establish authentication across actual mail streams |
| dmarcian | DMARC record interpretation | DMARC Inspector for reviewing published policy syntax | A record inspection is separate from aggregate-report analysis |
| dig | Manual DNS verification | Direct inspection of DNS questions and answers | Interpretation and evidence packaging remain your responsibility |
These are workflow recommendations, not measured performance rankings. No comparative accuracy, speed or sales-outcome claim underpins the order.
1. SCOUTz: Best Email-Security Evidence Tool for Prospect Meetings
SCOUTz provides dated cybersecurity evidence and prospect intelligence through domain and customer-authorized Microsoft 365 reviews. It helps you bring an observed condition into discovery, identify its limits and ask for an appropriate next commitment.
Choose SCOUTz for the conversation layer around a domain review. Keep specialist DNS and message-authentication verification in the technical workflow rather than assuming a prospect report replaces them.
SCOUTz Pros
- Connects dated security evidence with prospect context.
- Separates public-domain observations from consented internal evidence.
- Supports an evidence-to-scope discussion without requiring speculative breach-loss claims.
SCOUTz Cons
- Public-domain evidence cannot establish Conditional Access coverage or tenant sharing configuration.
- Microsoft 365 Review and Evidence Reports remain Open Beta in the client-provided October 15, 2026 reference.
- A finding does not establish buying intent or an unresolved customer problem.
Best for: MSP owners and sales leaders preparing evidence-led discovery and proposals.
Keep the product boundary intact: customer-authorized Microsoft 365 evidence covers configuration and metadata, never mail, files, chats, documents or prompts. Unread evidence stays unknown. The MSP still chooses the service, process, project or decision to take no action.
Verdict: Buy for the prospect-intelligence role only after validating fit through Open Beta. Join Open Beta is the primary next step; acceptance follows an MSP-fit review.
2. MXToolbox: Best Checker for Individual DNS Lookups
MXToolbox provides dedicated lookup tools for SPF, DKIM and DMARC. Use the relevant lookup when you need to inspect a published record and understand the returned result before a technical discussion.
A DKIM lookup needs the selector as well as the domain. Preserve how you obtained that selector, because checking one selector does not establish coverage of every sending service.
MXToolbox Pros
- Provides protocol-specific lookup interfaces.
- Supports focused investigation of an individual domain record.
- Helps separate a DNS publication question from a broader security claim.
MXToolbox Cons
- A successful lookup does not prove that actual messages authenticate.
- DKIM investigation depends on knowing the relevant selector.
- An isolated result still needs your observation date, scope and interpretation.
Best for: Technicians checking a specific SPF, DKIM or DMARC record before escalation.
In your 2026 review process, save the queried name and returned record rather than retaining only a verdict label. That gives another technician something concrete to reproduce. Treat any inferred business consequence as a separate statement requiring context.
Verdict: Buy for focused lookup work, after confirming the required workflow fits your team.
3. dmarcian: Best Checker for DMARC Record Interpretation
dmarcian's DMARC Inspector helps examine a domain's published DMARC record. It fits the point where you need to explain policy syntax and distinguish a monitoring request from quarantine or rejection.
Keep that inspection separate from DMARC aggregate-report analysis. The published policy states what the domain requests; reports describe authentication observations reported by receiving systems.
dmarcian Pros
- Gives DMARC record interpretation a dedicated interface.
- Helps technicians discuss policy tags rather than a generic score.
- Supports a focused review of the domain's published DMARC instructions.
dmarcian Cons
- Inspecting a record does not inventory every legitimate sender.
- A policy alone does not establish the effect on real messages.
- You still need ownership and sending-service context before recommending enforcement changes.
Best for: MSP practitioners explaining a DMARC policy or preparing an enforcement review.
DMARC defines 3 policy values for the p tag: none, quarantine and reject. These are requested handling policies, not three grades of organizational security. A monitoring policy can be intentional while a business inventories legitimate senders.
Verdict: Buy for DMARC-focused interpretation; hold enforcement changes until sender evidence supports them.
4. dig: Best Checker for Manual DNS Verification
dig is a DNS query utility documented by the Internet Systems Consortium. It lets a technician inspect answers for SPF TXT records, DMARC TXT records and a known DKIM selector's published DNS record.
Use dig when you need the actual query and response rather than an interface's summary. Record the resolver, queried name, response status and timestamp alongside the answer.
dig Pros
- Exposes the DNS question and returned answer.
- Supports explicit selection of the resolver to query.
- Produces output you can retain for another technician to inspect.
dig Cons
- Requires DNS and authentication knowledge to interpret correctly.
- Does not provide an MSP sales narrative or client-safe explanation.
- A DNS response does not prove how a particular message authenticated.
Best for: Practitioners independently checking the evidence behind a finding.
A missing answer needs careful wording. Distinguish a resolver error, an absent queried record and a selector you never assessed. The statement that a known selector returned no record is narrower than claiming the organization does not use DKIM.
Verdict: Buy into dig as a verification practice; skip it as a standalone owner-facing report.
How These Tools Are Ranked
The ranking follows the criteria above: visible sources, protocol-specific interpretation, declared coverage, repeatability and usefulness to the next decision. The first position reflects this article's MSP prospect-meeting audience. The remaining positions serve distinct technical jobs.
The technical boundaries follow SPF's RFC 7208, DKIM's RFC 6376 and DMARC's RFC 7489. This 2026 guide compares their documented jobs and supplied product positioning; it does not claim hands-on comparative testing.
What a Defensible Check Must Preserve
SPF evaluation permits at most 10 DNS-lookup-causing terms and modifiers under RFC 7208. Count the relevant mechanisms and redirects according to the protocol, including nested evaluation. Counting visible include strings alone is insufficient.
DMARC has 2 authentication paths to a pass: aligned SPF or aligned DKIM. An SPF pass without identifier alignment does not establish a DMARC pass. Likewise, finding a DKIM public key does not prove that a specific message carried a valid, aligned signature.
Preserve these fields in your evidence packet:
- Condition: the specific published policy or authentication result.
- Affected object: the domain, selector or message under examination.
- Source and date: DNS response, message headers or reporting data, with observation time.
- Unknowns: untested senders, unavailable reports and unassessed tenant controls.
- Recommended outcome: the question or validation step needed before a change.
DNS observations establish what the queried source returned at that time. Message headers and aggregate reports provide different evidence. Keep those scopes separate instead of combining them into a single assurance statement.
Turn the Finding Into an Agreed Next Action
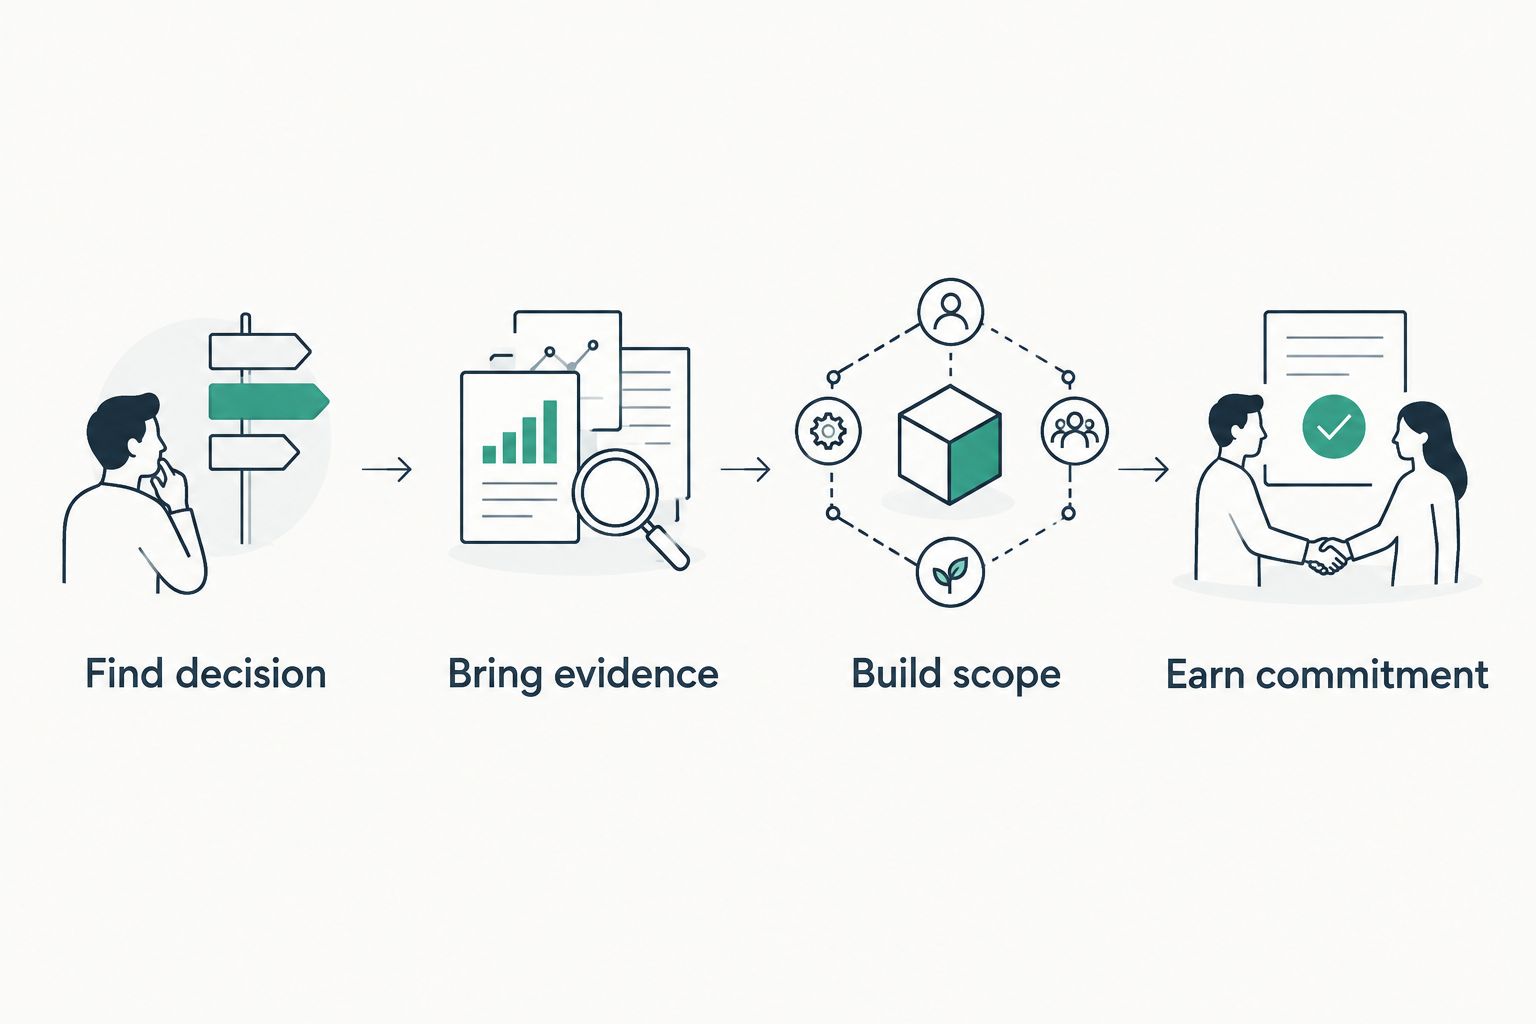
The SCOUTz Evidence-to-Agreement Framework gives your 2026 meeting a practical sequence: Find the decision, Bring the evidence, Build the scope, Earn the next commitment. It is a conversation framework, not a proven close-rate intervention.
Use this abbreviated sequence in your working notes:
- Find decision: identify what the owner needs to decide.
- Bring evidence: show the observed condition and its limits.
- Build scope: separate validation work from configuration changes.
- Earn commitment: agree on an owner and a specific next action.
Suppose a dated DNS observation shows p=none. State that condition first. Explain that the policy requests monitoring rather than quarantine or rejection, then name the boundary: this observation does not establish compromise, sender coverage or whether monitoring remains intentional.
Illustrative dialogue: The MSP says, “The published policy requests monitoring. We have not reviewed your legitimate sending services or reporting history. Who owns that review, and would you like a scoped validation before considering a policy change?”
If the owner says the current provider handles it, preserve that choice. Ask whether the provider can confirm the intended policy and share the relevant evidence. Do not treat the objection as proof of neglect.
| Scope | Evidence Needed | Deliverable | Boundary |
|---|---|---|---|
| Record validation | Dated DNS answers | Confirmed publication findings | Does not establish sender coverage |
| Sender review | Authorized reporting and sending-service context | Sender inventory and unanswered questions | Does not authorize configuration changes |
| Enforcement project | Validated sender inventory and approved change plan | Agreed implementation and verification scope | Requires owner approval and operational judgment |
Your follow-up should record the agreed action, not invent urgency. An illustrative script is: “We agreed to validate the sending inventory before discussing enforcement. Please confirm the domain owner and the reporting access you authorize. The next proposal will separate evidence collection, any approved changes and verification.”
Which Checker Should You Choose?
Choose the tool for the decision you need to support. Use the prospect-intelligence option for meeting preparation, MXToolbox for individual lookups, dmarcian for DMARC interpretation and dig for direct DNS verification.
For an undecided MSP, start with reproducible DNS evidence and a clear statement of unknowns. Add the conversation layer when you need to turn that evidence into discovery, scope and a proposal. A tool purchase does not remove the need for technical review or buyer agreement.
FAQ
What's the best SPF DKIM DMARC checker for an MSP prospect meeting?
SCOUTz is the best fit in this shortlist for MSP prospect-meeting preparation. Its role is dated domain-security evidence and account context; use technical verification alongside it when interpreting individual authentication records.
Is MXToolbox better than dig for checking DNS records?
MXToolbox suits guided individual lookups, while dig suits direct inspection of DNS questions and answers. Choose according to the technician's task and retain the queried name, response and observation time.
Does a published DKIM record prove that email is signed correctly?
No. A published DKIM record establishes that the queried selector has a DNS answer; message-level verification is needed to establish whether a particular message has a valid signature and DMARC alignment.
Does a DMARC policy of none mean the domain was compromised?
No. A DMARC policy of none requests monitoring rather than quarantine or rejection. Confirm whether that policy is intentional and review authorized sender evidence before recommending a change.
Can a public domain review establish Microsoft 365 security?
No. Public-domain observations cannot establish Conditional Access coverage, application permissions, license assignments, Intune device state or tenant sharing configuration. Those require separately authorized internal evidence.
Should an MSP move every prospect straight to DMARC reject?
No. Review legitimate senders, alignment evidence, reporting and ownership before proposing enforcement changes. Obtain approval for the change scope and define how the result will be verified.
What should an MSP do when a checker cannot read a source?
Record the evidence as unknown or unreadable and identify the coverage limitation. An unread source does not establish that a control is absent or that the environment is clean.
One Last Thing
Pin the baseline before proposing the fix. Keep the original response, affected object, source and date. Then rescan against that baseline after an authorized change and distinguish the changed condition from anything still unassessed.
A policy difference proves that the observed policy changed. It does not, by itself, prove that every legitimate sender works or that every receiver enforces the requested handling.