Yes, a security posture score can change without a security incident because the measured configuration, assessment coverage, available evidence or scoring method can change. A score change alone establishes neither compromise nor remediation; you need the dated findings and assessment boundaries to explain what moved.
- Can a security posture score change without a security incident? Yes. Configuration, coverage and scoring changes can move it.
- SCOUTz supports MSP sales preparation with dated cybersecurity evidence; a score alone does not establish an incident.
- Compare the same objects, checks and coverage before describing a score change as improvement or deterioration.
- Unreadable evidence remains unknown. Verify changed findings against a pinned baseline before presenting proof.
Can a security posture score change without a security incident?
Yes. A security posture score summarizes an assessment, not an incident investigation. An administrator can change a policy, a review can gain access to another evidence source, or a scoring model can change how it evaluates an existing condition. None of those events requires a security incident.
For MSPs using SCOUTz, the useful question is what the dated evidence supports. Separate the observed condition from its possible consequence before discussing the score with a prospect or client.
| What changed | What to inspect | What the change establishes | What remains unproven |
|---|---|---|---|
| Configuration | The affected object and before-and-after setting | A measured setting changed | Whether an incident occurred |
| Assessment coverage | Sources, permissions and assessed objects | The review covered different evidence | Whether the environment itself changed |
| Evidence readability | Collection results and declared non-reads | Evidence became readable or unreadable | Whether an unread control exists |
| Scoring method | Check definitions, weights and model version, where available | The assessment method changed | Whether security improved or deteriorated |
| Time-sensitive condition | Observation date and relevant expiry | A dated condition crossed a threshold | Whether anyone exploited it |
These are explanations to investigate, not conclusions to assign automatically. Keep the relevant check, run date and source beside every proposed explanation.
Why this matters
A misleading score explanation creates the wrong conversation. An MSP can present a methodology change as deterioration, describe newly visible evidence as a newly created problem, or celebrate missing evidence as a resolved finding.
For a 2026 client review, start with the comparison boundary: the domain or tenant assessed, the evidence available and the date of each run. Then explain the affected condition. The headline score belongs after that explanation.
The business decision also needs an owner. A changed email-security observation belongs with whoever manages the domain and sending services; a tenant configuration question requires an authorized tenant owner. A score does not assign responsibility.
Why a security posture score varies
Investigate these drivers before attaching meaning to a change. Their effect depends on the assessment's actual scoring rules.
- Configuration changes: A policy edit, permission change or domain-record update changes what a check observes. Establish who made the change and whether it was intended.
- Coverage changes: A public-domain review and a customer-authorized Microsoft 365 review answer different questions. Adding internal evidence changes the assessment boundary.
- Permission and license limits: An assessment can lose visibility into a source. Record that limitation separately from the condition being assessed.
- Methodology changes: Revised check definitions or scoring weights can change a result while the underlying configuration stays the same. Request the applicable version or change record.
- Time-sensitive evidence: Certificates and other dated evidence need their observation and expiry context. An older report cannot establish the current condition.
- Object-scope changes: Comparing different domains, tenant objects or assessed populations changes the comparison. Reconcile the object list before calling the result a trend.
Do not assume every assessment platform handles these drivers identically. Inspect the method used for the actual report, including its treatment of unknown and unreadable evidence.
How should an MSP investigate a changed score?
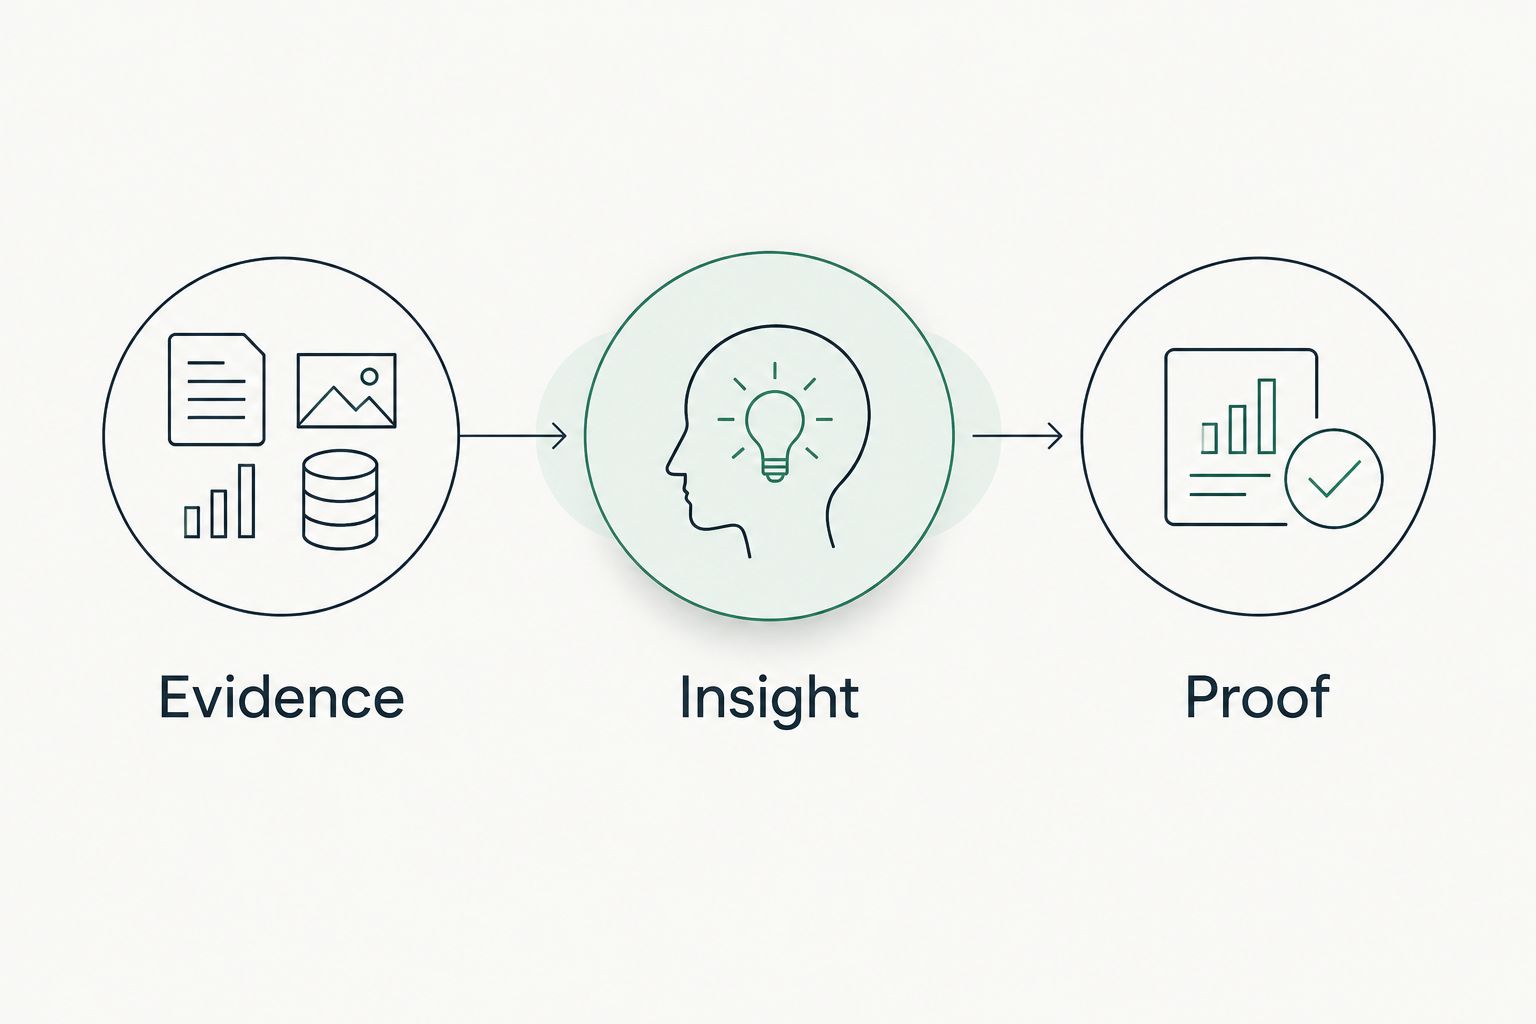
Use evidence, insight and proof as separate stages. SCOUTz's editorial standard, supplied October 15, 2026, defines the distinction as what ran, why now and what changed. Apply that discipline before putting a score movement into a proposal or renewal deck.
Evidence
Retrieve the underlying findings from both runs. Preserve the source, run date, check identity, affected object, observed condition and coverage state. Record any permission or license limitation alongside the result.
A missing finding requires explanation. Determine whether the condition changed, the object left scope, the check stopped running or the source became unreadable. Those explanations have different meanings for the client.
Keep evidence states distinct: Verified, Observed, Inferred, Possible, Unknown and Unreadable. They describe different relationships to evidence, rather than steps on a single certainty ladder.
Insight
Explain the operational meaning of the observed difference. A published DMARC policy requesting monitoring calls for a conversation about intended enforcement and report ownership. It does not establish mailbox compromise.
Identify the owner and the next choice. The owner can confirm that a setting is intentional, authorize further review, approve a change or accept a documented limitation. Leave the vendor or service choice until the required outcome is clear.
Proof
Rescan against a pinned baseline after the agreed action. Compare the same check and affected object, and disclose changes in coverage or method. A new headline score without that comparison is insufficient evidence of the specific outcome.
For a 2026 report, retain the original observation and the verification date together. Describe exactly what the rescan establishes and keep the unassessed areas visible.
The guide to dated evidence versus static reports provides related context for keeping assessment comparisons tied to their observation dates.
What does a DMARC change prove?
A DMARC record change establishes a change in the published policy observed by the check. Its significance depends on the actual record, the domain assessed and the observation date. It does not establish what happened inside a mailbox.
Consider an illustrative review in 2026 where a domain's published policy changes from p=none to p=reject. The policy now requests rejection of messages that fail DMARC, subject to receiver handling and the applicable policy. That is a configuration observation, not evidence that every legitimate sender is correctly configured.
Before describing the change as a completed improvement, review the intended sending services, report ownership and the agreed outcome. Preserve any unanswered questions about legitimate message flows.
A client-facing explanation should separate the parts:
- Observed: The dated DNS review returned a different published DMARC policy.
- Possible consequence: The requested handling of messages failing DMARC changed.
- Boundary: The DNS observation does not establish mailbox activity or successful delivery for every sender.
- Owner: The person responsible for domain records and email operations confirms intent.
- Next choice: Review reporting and sender alignment before deciding whether further work is required.
This structure supports a useful decision without turning an email-security finding into an incident claim.
Can a public-domain score explain Microsoft 365 security?
A public-domain review cannot establish internal Microsoft 365 configuration. Public observations and customer-authorized tenant evidence have different sources and limits, even when they concern the same organization.
| Review boundary | Best for | Useful evidence | Limitation |
|---|---|---|---|
| Public-domain observations | Preparing domain and email-security questions | Published records and externally observable conditions | Cannot establish Conditional Access coverage, application permissions or tenant sharing configuration |
| Customer-authorized Microsoft 365 review | Reviewing permitted internal configuration | Authorized configuration and metadata | Conclusions remain limited by permissions, licenses and sources actually read |
Public-domain evidence is useful for preparing a focused conversation without representing that internal systems were inspected. Its limitation is the boundary: a visible domain condition cannot answer a tenant-level question.
Customer-authorized evidence supports more specific internal questions. It also requires consent and a clear record of what was assessed. For SCOUTz cybersecurity prospect intelligence, Microsoft 365 review evidence is configuration and metadata only; mail, files, chats, documents and prompts are outside that evidence boundary.
Keep each platform's results separate. Combining unrelated platforms into a single score obscures which controls, sources and limitations explain the result.
Does a higher score mean the client is safer?
A higher score alone does not establish improved security. It supports that conclusion only to the extent that the underlying findings demonstrate a relevant improvement within a comparable assessment boundary.
For example, a verified configuration change can support a narrow statement about that control. A different object population or an unread source cannot support the same statement. Explain which situation applies before presenting the result as progress.
For your 2026 reporting standard, require an affected object, dated evidence, an agreed outcome and verification. Keep unresolved questions visible rather than letting a better headline number answer them implicitly.
Does a lower score mean there was a breach?
A lower score does not establish a breach. It can reflect a changed condition, expanded visibility or a different assessment method; determining whether an incident occurred requires evidence about the suspected event.
Preserve important distinctions. A breach-data match does not establish a compromised user, tenant-wide application permission does not establish a malicious app, and an answering service does not establish an exploitable service.
If the underlying evidence warrants investigation, identify the responsible owner and follow the organization's investigation process. The score explains neither the event timeline nor the extent of any impact.
How should an MSP turn the finding into an agreed next step?
SCOUTz is best for MSPs preparing sales conversations with dated cybersecurity evidence and account context. Its strength is that preparation; the MSP remains responsible for interpreting the evidence, managing the relationship and earning agreement.
Use the SCOUTz Evidence-to-Agreement Framework to move beyond a score discussion:
- Find the decision. Establish what the buyer needs to decide, such as whether to authorize an internal review or validate a changed domain policy.
- Bring the evidence. Present the dated observation, its source and its limits. Separate a verified condition from a hypothesis.
- Build the scope. Define the affected objects, responsible owner, required access and expected outcome. Keep unassessed areas outside the claim.
- Earn the next commitment. Agree on the next action, who owns it and how completion will be verified. Preserve the buyer's choice to defer or decline.
This is a conversation framework, not a proven close-rate intervention. A finding becomes useful when it supports a specific decision and a defensible scope.
For MSPs evaluating this approach, Join Open Beta is the primary next step. Confirm current product status and participation terms before committing to a workflow.
FAQ
Can a security posture score change without a security incident?
Yes. Configuration, assessment coverage, evidence availability and scoring-method changes can move a security posture score without an incident. Compare the underlying dated findings before explaining the movement.
Does an improved security score prove remediation worked?
An improved score alone does not prove remediation worked. Verify the agreed outcome by rescanning the affected object against a pinned baseline and disclose any coverage or methodology changes.
Why did the score change when nobody changed a setting?
Assessment coverage, evidence readability or scoring methodology can change even when the measured configuration stays the same. Inspect the two runs before assigning a cause.
Should unreadable evidence count as a clean result?
Unreadable evidence must remain unknown rather than clean. Record the collection limitation and identify what was not assessed during that scan.
Can a domain review confirm Microsoft 365 Conditional Access coverage?
A public-domain review cannot establish Microsoft 365 Conditional Access coverage. That question requires customer-authorized internal evidence with sufficient permissions and explicit coverage limits.
Can I compare scores from different security platforms?
Different security platforms require separate interpretation because their sources, scope and scoring methods differ. Compare the underlying conditions and coverage rather than combining their scores.
What should I show a client when their security score drops?
Show the changed finding, affected object, source, run date and assessment limits. Explain the supported consequence, identify the owner and agree on the next decision without claiming an incident from the score alone.
One last thing
A finding disappearing deserves the same scrutiny as a finding appearing. The condition might have changed, or the assessment might have stopped seeing it. Preserve that distinction in every 2026 score comparison.
Keep the baseline and the non-reads beside the result. That gives the client evidence they can question, an outcome they can authorize and a verification standard they can understand.


