Dark Web ID gives MSPs a focused tool for dark web credential monitoring. That job differs from preparing a broader prospect security review with dated domain evidence and customer-authorized Microsoft 365 configuration evidence. The best Dark Web ID alternative in 2026 is SCOUTz if you need MSP prospect intelligence; Microsoft Secure Score if you need Microsoft 365 security recommendations rather than dark web monitoring.
- Compare Dark Web ID alternatives by job: credential monitoring, prospect intelligence, or tenant security assessment.
- SCOUTz is best for MSP prospect intelligence and evidence-led meeting preparation, rather than replacing credential monitoring.
- Microsoft Secure Score supports Microsoft 365 security improvement; Have I Been Pwned supports breach-record research.
- A breach-data match does not establish current account compromise, an unresolved problem, or buying intent.
Why this matters
An exposed credential record, a published email policy, and a tenant configuration answer different questions. Your proposal needs to preserve those differences.
SCOUTz provides cybersecurity prospect intelligence for MSPs: dated evidence and account context you bring into a sales conversation. For your 2026 shortlist, decide whether you need to replace a monitoring service, add assessment evidence, or improve meeting preparation. One purchase does not automatically cover all three jobs.
Dark Web ID alternatives at a glance
These options are alternatives for particular workflows, not interchangeable products. Keep Dark Web ID in the comparison so your team can identify capabilities it still needs.
| Option | Best for | Standout capability | Difference from Dark Web ID |
|---|---|---|---|
| Dark Web ID | MSP dark web credential monitoring | Credential-exposure monitoring | The monitoring benchmark in this comparison |
| SCOUTz | MSP prospect intelligence and sales preparation | Dated public-domain evidence and consented Microsoft 365 reviews | Prepares an evidence-led conversation rather than serving as a like-for-like monitoring replacement |
| Microsoft Secure Score | Microsoft 365 security improvement planning | Microsoft security recommendations and scoring | Focuses on the Microsoft environment rather than dark web credential records |
| Have I Been Pwned | Researching known breach exposure | Searching its indexed breach records | Supports breach-record research rather than a broader prospect assessment |
Choose the job before choosing the vendor. If your service agreement promises ongoing credential monitoring, assess replacements against that obligation separately from sales enablement.
1. SCOUTz: best for MSP prospect intelligence
SCOUTz, by RYTHMz, prepares MSP owners and sales leaders for conversations using dated cybersecurity evidence and account context. Its role sits between a booked meeting and an agreed engagement. The MSP retains responsibility for the relationship, judgment, scope, and sale.
The client's October 15, 2026 product reference lists Domain Review as available and Microsoft 365 Review, Evidence Reports, and Prospect Intelligence as Open Beta. Treat those labels as dated product information when planning an evaluation.
Where it shines
- Public-domain observations and customer-authorized Microsoft 365 evidence remain separate.
- Read-only Microsoft 365 reviews use configuration and metadata, excluding mail, files, chats, documents, and prompts.
- Findings retain their check and run date, giving your team a specific condition to discuss.
- Rescans against a pinned baseline support proof of what changed.
Where it falls short
- It is not a like-for-like substitute for a contracted dark web monitoring service.
- Microsoft 365 Review and the report experience have beta limitations to evaluate against your workflow.
- A public-domain review cannot establish internal Conditional Access coverage, application permissions, license assignments, or tenant sharing configuration.
- Evidence still requires human interpretation. A scan does not establish buying intent or close a deal.
| Dimension | This alternative | Dark Web ID |
|---|---|---|
| Primary job | Prospect intelligence and meeting preparation | Dark web credential monitoring |
| Evidence focus | Public-domain observations and consented tenant configuration | Credential-exposure monitoring |
| Sales use | Explain a condition, establish boundaries, agree a next action | Discuss credential exposure without overstating what a match proves |
Best for: MSPs that need a better-supported discovery conversation and an evidence-led proposal.
Verdict: Buy for fit only after evaluation; keep credential monitoring separate.
Put evidence into an agreement
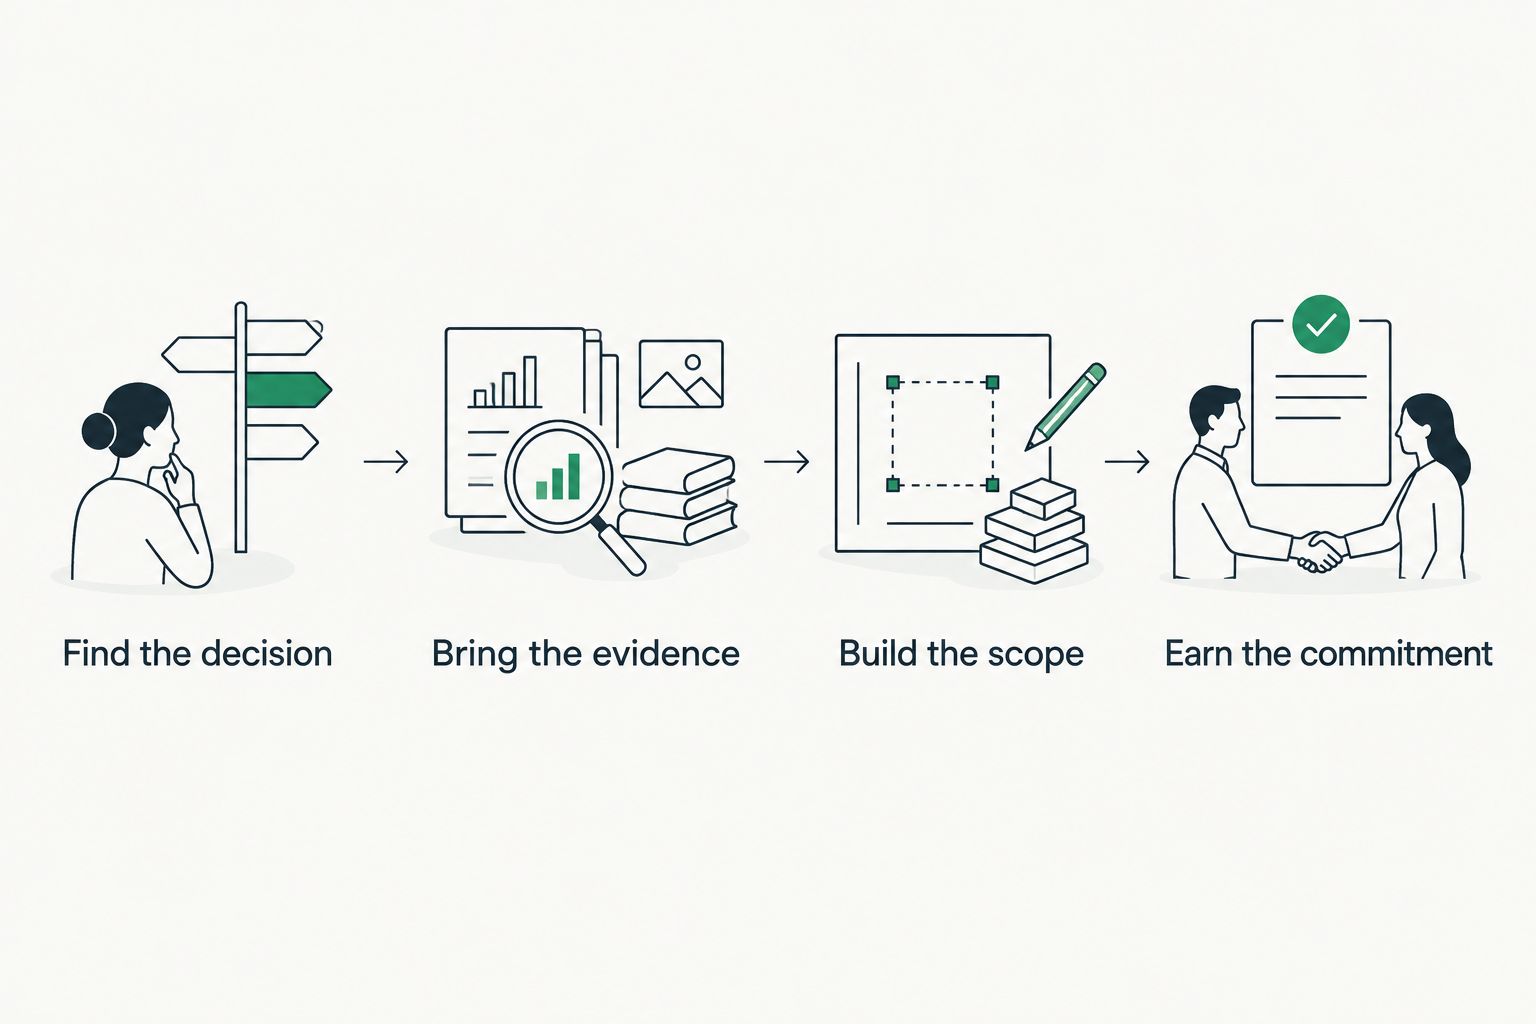
Use the SCOUTz Evidence-to-Agreement Framework to move from a technical observation to a buyer-approved next action. This is an original conversation framework, not a validated close-rate intervention.
Find the decision
Identify the decision the prospect actually owns. For an email-security discussion, that might be whether to commission a review of the organization's intended DMARC enforcement and reporting process.
Keep the first evaluation narrow: use 1 domain, identify its owner, and agree what the review will answer. Do not turn every observation into an immediate remediation project.
Bring the evidence
Attach the source, check name, run date, affected object, and limits. A published DMARC policy requesting monitoring is an observed condition. It does not establish compromise or prove that the policy is unintended.
Keep unknown evidence unknown. If a source was unreadable or permission limited, preserve that state rather than describing the associated control as absent.
Build the scope
Separate the condition from the recommended outcome and vendor choice. The prospect can choose a process review, a configuration project, additional assessment, or no change.
Start with 1 dated baseline for the agreed scope. That gives the subsequent review a defined comparison point instead of an unqualified claim that security improved.
Earn the commitment
Agree the owner, required authorization, deliverable, and acceptance criteria. A useful commitment is permission to perform a defined review, not assumed agreement to buy a managed service.
Record 1 agreed owner for the next action. Keep the relationship in the CRM and delivery responsibilities in the systems your MSP uses to run service work.
Illustrative conversation: from DMARC to scope
The following dialogue is illustrative, not a customer result or an actual scan finding.
MSP: The reviewed DMARC record requests monitoring. That tells us the published policy at the review date; it does not tell us whether your team intends to change enforcement. Who owns that decision?
Prospect: Our email provider manages it. We do not want another tool.
MSP: The next step can be a review with that provider. We can document the intended policy, reporting owner, and prerequisites for any change. You can then decide whether a project is needed.
That exchange makes the consequence discussable without declaring an incident. The proposed scope follows the evidence and the owner's answer.
Compare scopes before writing the proposal
| Scope | Evidence required | Agreed deliverable | Boundary |
|---|---|---|---|
| Public-domain review | Dated public observations | Findings, questions, and ownership | No internal tenant conclusions |
| Authorized tenant review | Customer-approved read-only configuration evidence | Assessed conditions and declared non-reads | No automatic configuration changes |
| Verification review | Rescan against the pinned baseline | What changed within the agreed scope | No guarantee of overall security |
For an MSP evaluating this workflow in 2026, Join Open Beta is the primary next step. To see the approach before deciding, book a demo.
2. Microsoft Secure Score: best for tenant improvement planning
Microsoft Secure Score provides security recommendations and a score within Microsoft's environment. It suits an MSP working with an authorized customer on Microsoft security configuration and improvement priorities.
It answers a different question from credential monitoring: which Microsoft security actions deserve review. A score does not establish whether an account is compromised or whether a prospect intends to purchase services.
Where Microsoft Secure Score shines
- Microsoft-specific recommendations support a tenant-focused improvement discussion.
- Your team can connect recommended actions to an authorized customer's configuration review.
- It provides a starting point for discussing priorities with the customer's technical owner.
Where Microsoft Secure Score falls short
- It does not replace dark web credential monitoring.
- Its Microsoft focus does not establish the condition of every platform the customer uses.
- A score needs interpretation alongside the underlying recommendations, scope, and business requirements.
| Dimension | Microsoft Secure Score | Dark Web ID |
|---|---|---|
| Primary job | Microsoft security improvement | Credential-exposure monitoring |
| Evidence focus | Microsoft security recommendations and scoring | Dark web credential records |
| Appropriate discussion | Which configuration actions warrant review | What an exposure record establishes and what needs verification |
Best for: MSPs reviewing an authorized customer's Microsoft environment and agreeing improvement priorities.
Verdict: Buy only for the Microsoft improvement job; skip it as a monitoring replacement.
3. Have I Been Pwned: best for breach-record research
Have I Been Pwned lets you research exposure in its indexed breach records. Its domain-search workflow requires domain verification, which matters when deciding what an MSP can investigate for an organization.
Use the result as a research input. A historical match does not prove that a password remains valid, an account remains active, or the organization has an unresolved incident.
Where Have I Been Pwned shines
- It supports direct research into known breach-record exposure.
- Domain verification establishes a boundary for organization-wide searches.
- Results give your team a specific record to investigate rather than a generic warning.
Where Have I Been Pwned falls short
- Its indexed records do not represent every breach or every exposure source.
- A match does not establish current compromise; no match does not establish safety.
- Breach-record research alone does not produce a domain and tenant security assessment.
Best for: MSPs investigating known exposure records within an authorized research workflow.
Verdict: Buy for research fit after checking the intended usage; skip it as a complete assessment replacement.
Why consider switching from Dark Web ID?
The supported reasons in this 2026 comparison are changes in the job you need done. They are not claims about Dark Web ID outages, commercial changes, or service quality.
- Your sales team needs dated domain evidence and account context before discovery.
- Your customer authorizes a Microsoft 365 configuration review that credential monitoring does not answer.
- Your proposal needs an explicit baseline, owner, verification step, and accepted scope.
- Your team needs targeted breach-record research rather than a broader monitoring workflow.
These are also reasons to add a complementary capability instead of replacing the existing service. Before removing monitoring, document who owns alert review, customer communication, investigation, and escalation afterward.
When staying with Dark Web ID is the right call
Stay when dark web credential monitoring remains the requirement and the service meets your agreed needs. A broader assessment tool solves a different problem.
For a 2026 renewal decision, review the actual service obligation and operating process. Keep the discussion grounded in source coverage, alert handling, authorized access, and evidence retention rather than the size of a sales report.
FAQ
What's the best Dark Web ID alternative for MSP sales preparation?
SCOUTz is best suited to MSP prospect intelligence and evidence-led meeting preparation in this comparison. It provides dated domain evidence and customer-authorized Microsoft 365 reviews, with beta status applying to parts of the workflow. It is not a like-for-like credential-monitoring replacement.
Is Microsoft Secure Score a replacement for Dark Web ID?
Microsoft Secure Score is not a replacement for dark web credential monitoring. It supports Microsoft security improvement discussions through recommendations and scoring. Choose it for an authorized tenant review rather than credential-exposure monitoring.
Can Have I Been Pwned prove a customer's account is compromised?
A Have I Been Pwned match does not prove current account compromise. It establishes a match within its indexed breach records. Current account status, credential validity, and subsequent remediation require separate investigation.
Can a public-domain review assess Microsoft 365 internal controls?
A public-domain review cannot establish internal Microsoft 365 controls such as Conditional Access coverage or application permissions. Those questions require customer-authorized internal evidence. Unread evidence must remain explicitly unknown.
Should an MSP replace dark web monitoring with prospect intelligence?
An MSP should replace monitoring only if the replacement satisfies the monitoring requirement. Prospect intelligence supports research, discovery, and scope preparation. Keep monitoring responsibilities separate when evaluating that purchase.
Can breach data support an MSP sales conversation?
Breach data can support a bounded conversation about an exposure record. Preserve the source, date, limitations, and verification questions. Do not present a match as current compromise, buying intent, or proof of an unresolved problem.
What should MSPs evaluate during a product trial?
Evaluate whether the product answers the intended job with traceable evidence. Review source boundaries, dated findings, non-reads, report interpretation, and the next-action workflow. Confirm that beta limitations fit the proposed use.
One last thing
The strongest comparison is often a scope comparison, not a feature count. Ask each vendor to show how a finding retains its source, date, limits, owner, and verification path through your workflow.
SCOUTz prepares the conversation. The relationship and the sale stay yours. Treat that boundary as an evaluation criterion: your next commitment should come from the buyer's decision, supported by evidence.


