Inforcer’s strength is managing Microsoft 365 policies across customer tenants. That delivery job differs from preparing evidence for a prospect meeting before your MSP has an ongoing management relationship. The best choice among inforcer alternatives in 2026 is SCOUTz for prospect intelligence and sales preparation; CIPP for hands-on Microsoft 365 administration.
- Compare inforcer alternatives by job: prospect intelligence, Microsoft 365 administration, or cross-tenant policy management.
- SCOUTz is best for MSP prospect intelligence and evidence-led sales preparation, not automatic configuration changes.
- CIPP suits hands-on tenant administration; Microsoft 365 Lighthouse suits Microsoft-native oversight within its eligibility requirements.
- Keep Inforcer when cross-tenant policy management remains the requirement.
Why this matters
Replacing a policy-management platform with a sales-preparation platform leaves a delivery gap. Buying another administration tool when your real problem is weak discovery leaves the sales problem untouched.
Start your 2026 evaluation with the decision you need to support. A prospect conversation needs dated observations, clear limits and an agreed next action. A managed tenant needs operational ownership, authorized changes and verification.
These jobs can share evidence. They still require separate acceptance criteria.
Inforcer alternatives at a glance
The table compares jobs rather than declaring a universal winner. Microsoft 365 administration, policy management and prospect intelligence overlap at the evidence layer, but their primary outputs differ.
| Tool | Best for | Standout capability | Difference from Inforcer |
|---|---|---|---|
| Inforcer | Cross-tenant Microsoft 365 policy management | Centralized policy deployment and management | Benchmark when repeatable tenant configuration is the requirement |
| SCOUTz | MSP prospect intelligence and sales preparation | Dated public-domain evidence and customer-authorized Microsoft 365 reviews | Prepares conversations through read-only evidence rather than automatic configuration changes |
| CIPP | Hands-on Microsoft 365 administration | Open-source, multi-tenant administration | Broader administration approach with hosting and operational responsibilities to evaluate |
| Microsoft 365 Lighthouse | Microsoft-native multi-tenant oversight | Microsoft’s MSP-focused tenant management experience | A Microsoft-native option whose fit depends on tenant eligibility and supported workloads |
For every option, ask the vendor or project to demonstrate your actual workflow. A feature name does not establish permission coverage, evidence quality or suitability for your customer base.
1. SCOUTz: best for prospect intelligence and sales preparation
SCOUTz cybersecurity prospect intelligence gives MSPs dated evidence and account context for discovery, proposals and client conversations. Its job sits between a booked meeting and an agreed scope. The MSP retains responsibility for the relationship and the sale.
The distinction from Inforcer is the intended outcome. You use a read-only review to establish what was observed, explain its limits and decide what to discuss. You do not use it to deploy a tenant configuration.
Where it shines
- Public-domain observations and customer-authorized Microsoft 365 evidence remain separate.
- Microsoft 365 review uses configuration and metadata, without reading mail, files, chats, documents or prompts.
- Findings retain their check and run date, giving the MSP a basis for explaining what ran.
- Rescans against a pinned baseline provide a way to show what changed.
Where it falls short
- Read-only review makes no automatic configuration changes. You still need delivery tooling and an authorized change process.
- Public-domain evidence cannot establish Conditional Access coverage, application permissions, license assignments or device state.
- The client’s October 15, 2026 product reference identifies Microsoft 365 Review and Evidence Reports as Open Beta, with multi-client and report experiences under beta validation.
- A finding does not establish buying intent, a confirmed breach or an unresolved customer problem.
Head-to-head: evidence preparation versus policy management
| Dimension | Prospect-intelligence approach | Inforcer |
|---|---|---|
| Primary job | Prepare an evidence-led conversation | Manage Microsoft 365 policies across tenants |
| Configuration changes | Read-only review; no automatic changes | Policy deployment and management |
| Prospect starting point | Public-domain observations, followed by authorized cloud review | An authorized tenant-management relationship |
| Acceptance test | Source, run date, limits and a useful next question | Required policy workflow demonstrated against your tenant needs |
Best for: MSP owners and sales leaders who need evidence for discovery and scope-building rather than another configuration-management console.
Verdict: Buy for the prospect-intelligence job after validating the beta workflow; skip as a replacement for policy deployment.
2. CIPP: best for hands-on Microsoft 365 administration
CIPP, the CyberDrain Improved Partner Portal, is an open-source Microsoft 365 administration project built for multi-tenant work. It belongs on your shortlist when technicians need an administration workspace and your MSP is prepared to own the associated operating decisions.
Evaluate CIPP against the administration tasks your team performs. Do not treat an open-source license as evidence that deployment, maintenance or support will require no effort.
Where CIPP shines
- Its open-source model lets your technical team inspect the project and evaluate its approach.
- Its multi-tenant administration focus fits technician-led Microsoft 365 workflows.
- You can assess specific administrative tasks rather than buying around a sales-reporting promise.
Where CIPP falls short
- You must decide who owns hosting, updates, access and operational support for your chosen deployment model.
- Administrative capability alone does not establish a client-safe sales narrative or an agreed proposal scope.
- Your team must validate the specific policy workflows it would replace before retiring Inforcer.
Best for: Technically involved MSPs seeking an open-source administration approach and willing to assess its operating responsibilities.
Verdict: Buy only after a task-level pilot; hold if nobody owns the operating model.
3. Microsoft 365 Lighthouse: best for Microsoft-native oversight
Microsoft 365 Lighthouse is Microsoft’s multi-tenant management experience for MSPs. It is a relevant alternative to investigate when your decision starts with Microsoft-native oversight rather than prospect research.
Tenant eligibility, licensing and supported capabilities determine fit. Check those requirements against your customer roster before treating Lighthouse as a replacement.
Where Microsoft 365 Lighthouse shines
- It provides a Microsoft-native starting point for supported multi-tenant management workflows.
- Its tenant-focused approach suits reviews of existing managed customers.
Where Microsoft 365 Lighthouse falls short
- Eligibility and supported workloads constrain the customers and tasks you can cover.
- Microsoft-native management does not establish feature parity with Inforcer’s policy workflows.
- A management view still needs interpretation before it becomes a buyer-facing recommendation.
Best for: MSPs evaluating supported Microsoft-native management workflows across eligible tenants.
Verdict: Buy into the workflow after checking eligibility; hold if essential customer coverage remains unconfirmed.
Why people switch from Inforcer
A justified switch starts with a changed requirement. The reasons below are decision criteria, not claims about measured customer churn, outages or vendor pricing changes.
The missing job is sales preparation
If your team can administer tenants but struggles to explain why a prospect should authorize the next assessment, another management console addresses the wrong problem.
Define the output instead: an observation with a source and date, a bounded implication, an owner question and a proposed next action. That is a different acceptance test from deploying a policy.
Your team wants a different administration model
An MSP considering CIPP should compare technical ownership, hosting, access controls and the actual tasks technicians perform. Test the replacement against a documented workflow.
Keep Inforcer until the replacement demonstrates the required work. An attractive feature list is insufficient migration evidence.
Microsoft-native coverage fits the customer roster
Lighthouse deserves evaluation when its supported workflows match your customers and service model. Verify eligibility before planning a change.
For a 2026 shortlist, record each requirement as demonstrated, partial or unconfirmed. Keep an unconfirmed feature out of the replacement case until someone demonstrates it.
Turn the comparison into an agreed next action
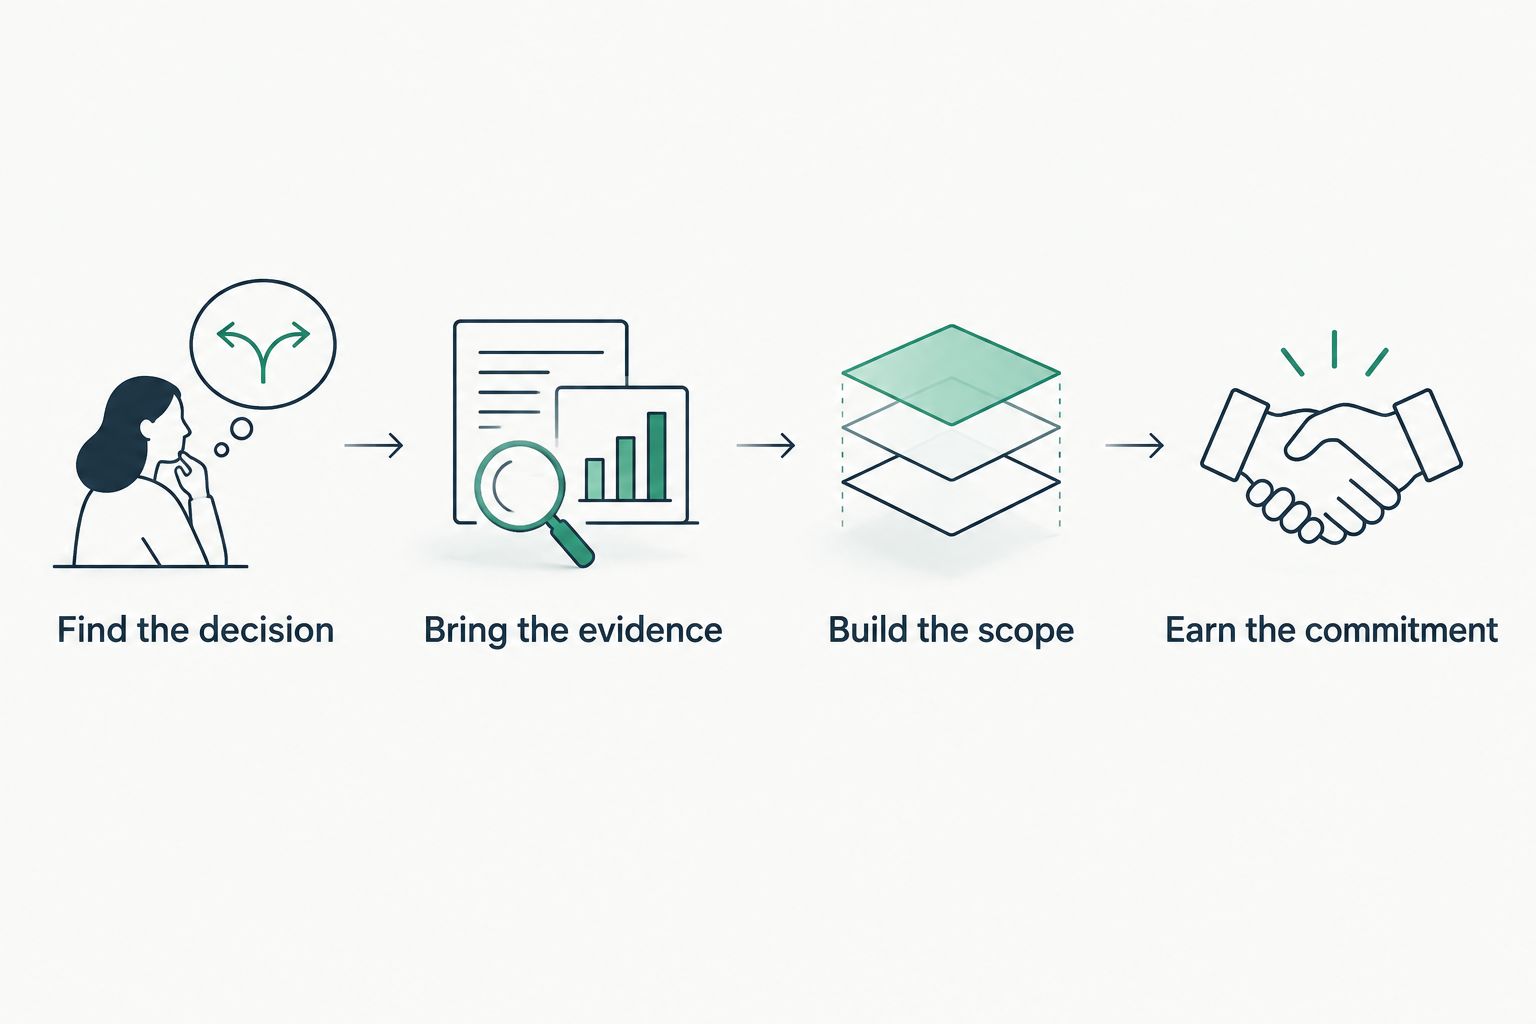
For sales-focused evaluations, use the SCOUTz Evidence-to-Agreement Framework: Find the decision, Bring the evidence, Build the scope, Earn the next commitment. It is a conversation framework, not a validated close-rate intervention.
Use these 4 decision steps to test whether a tool helps your MSP reach a clear next action without overstating evidence.
Find the decision
Establish what the prospect is deciding. That might be whether to authorize a Microsoft 365 review, commission a scoped project or leave the current arrangement unchanged.
Do not infer that decision from a public event, an email open or a security observation. Ask the buyer to confirm it.
Bring the evidence
Keep 3 evidence fields visible: source, run date and limits. Also identify the affected object and distinguish an observation from an inference.
Keep 2 evidence sources separate: public-domain observations and customer-authorized internal review. A domain review cannot establish tenant-wide Conditional Access coverage.
Build the scope
Translate the condition into a bounded outcome. If a published DMARC policy requests monitoring only, establish whether that remains intentional before recommending enforcement changes.
Keep the outcome separate from the vendor choice. The appropriate response can be a product, service, process, project or no change.
Earn the commitment
Ask for permission to take the next defined step. Record who owns it, what evidence it needs and what decision follows.
A buyer’s agreement to review evidence is narrower than agreement to remediation or an ongoing contract. Preserve that distinction in your follow-up.
Illustrative objection handling
The following dialogue is illustrative, not a customer account or an observed finding.
Prospect: Our current provider already handles email security.
MSP: That helps establish ownership. If a dated review shows a monitoring-only DMARC policy, the next step is to confirm the intended policy with that provider. Would you like to review that question together?
Prospect: We do not want configuration changes during an assessment.
MSP: We can scope a read-only review. Any proposed change would require a separate decision and authorization.
The conversation moves toward permission and scope. It makes no claim that the current provider failed or that a compromise occurred.
Illustrative follow-up script
Use this structure only after replacing the general condition with an actual, checked observation:
Thank you for reviewing the evidence. The next proposed action is to confirm whether the observed configuration remains intentional with its current owner. The review does not establish compromise or the effectiveness of controls outside its coverage. Please confirm whether you want to authorize that follow-up before any change is proposed.
For your 2026 evaluation, ask each shortlisted tool to support this handoff without losing the source, date or assessment boundary.
Join Open Beta
Explore evidence-led prospect preparation and the customer-authorized Microsoft 365 review workflow.
When staying with Inforcer is the right call
Stay with Inforcer when cross-tenant policy management remains the job you need done. A prospect-intelligence platform does not replace that operational responsibility.
Keep your evaluation specific. Confirm the policies, exceptions, access model and change workflow your team requires. Judge the incumbent and alternatives against the same documented tasks.
Adding a separate evidence-preparation workflow can be more appropriate than replacing a functioning delivery tool. Keep the relationship owner, assessment owner and change owner explicit.
FAQ
What are the best Inforcer alternatives for MSPs in 2026?
The best alternative depends on the job: SCOUTz for prospect intelligence and sales preparation, CIPP for hands-on Microsoft 365 administration, and Microsoft 365 Lighthouse for supported Microsoft-native oversight. Keep Inforcer on the comparison when cross-tenant policy management remains essential.
Is a prospect-intelligence platform a direct replacement for Inforcer?
No. A read-only prospect-intelligence platform prepares evidence and conversations, while Inforcer focuses on Microsoft 365 policy management. Evaluate those jobs separately.
Is CIPP better than Inforcer?
CIPP is a relevant choice when you want an open-source, multi-tenant administration approach. Whether it replaces Inforcer depends on demonstrated policy workflows and your willingness to own the chosen deployment model.
Can Microsoft 365 Lighthouse replace Inforcer?
Microsoft 365 Lighthouse is a replacement candidate only when eligible tenants and supported workflows cover your requirements. Validate the actual customer roster and administrative tasks before switching.
Can a public-domain scan establish Microsoft 365 security coverage?
No. Public-domain observations cannot establish Conditional Access coverage, application permissions, license assignments, Intune device state or tenant sharing configuration. Those questions require appropriately authorized internal evidence.
Does a security finding prove a prospect needs remediation?
No. A finding establishes a bounded condition within the evidence collected. Confirm its date, intended configuration, current owner and assessment limits before recommending action.
What should an MSP test before changing tools?
Test the exact job you need the replacement to perform. For management, demonstrate required administrative workflows; for sales preparation, demonstrate dated evidence, explicit limits and a useful handoff to an agreed next action.
One last thing
The most useful evaluation artifact is a declared non-read. It shows where the evidence stops.
Before selecting an alternative, ask for a review with permission-limited or unreadable evidence. Check that the report labels the gap instead of implying the control is absent or healthy. Then ask the salesperson to explain it without inventing urgency.
That exercise tests both the evidence boundary and the conversation your MSP will have with a buyer.


